
Standoff 12 · 2023
1stplace in the Silver League
10th place overall
Offensive security
team.
Penetration testing, red teaming and research. We assess real systems and turn hypotheses into reproducible results.
We approach security as an applied engineering problem: measurable conditions, testable hypotheses and results that can be reproduced and explained. Our practice combines penetration testing, vulnerability analysis and red teaming within the agreed scope and rules of engagement. We focus on real systems, precise testing and reproducibility: from an observation to a verified result.
We brought together offensive security specialists from different companies to tackle challenges that demand more than one skilled individual.
Practice is our common language. In cyber exercises, we attacked and held infrastructure; at Standoff, we competed for results and helped other teams grow. This experience shapes our approach to penetration testing, red teaming and research: precise testing, coordinated teamwork and reproducible results.
Standoff 12 · 2023
1st10th place overall
Standoff 17 · 2025
9thExperience in competitive cyber exercises
Standoff 14 · 2024
2Sharing experience, helping others grow
KiberS formed as a group of security testing specialists from different companies. It began with enthusiasts brought together by hands-on practice, an interest in offensive security and a commitment to maintaining a high technical standard.
Our starting point was the SOC Forum 2023 cyber battle. In an adversarial exercise, the team carried out attacks while holding infrastructure. It was our first full-scale test of coordinated teamwork.
The team then qualified for Standoff 12 (2023), taking 1st place in the Silver League and 10th overall. This earned us an invitation to the next event.
At Standoff 13 (2024), the team competed under updated rules and finished 11th. That year, we also returned to SOC Forum 2024 and mentored two teams at Standoff 14.
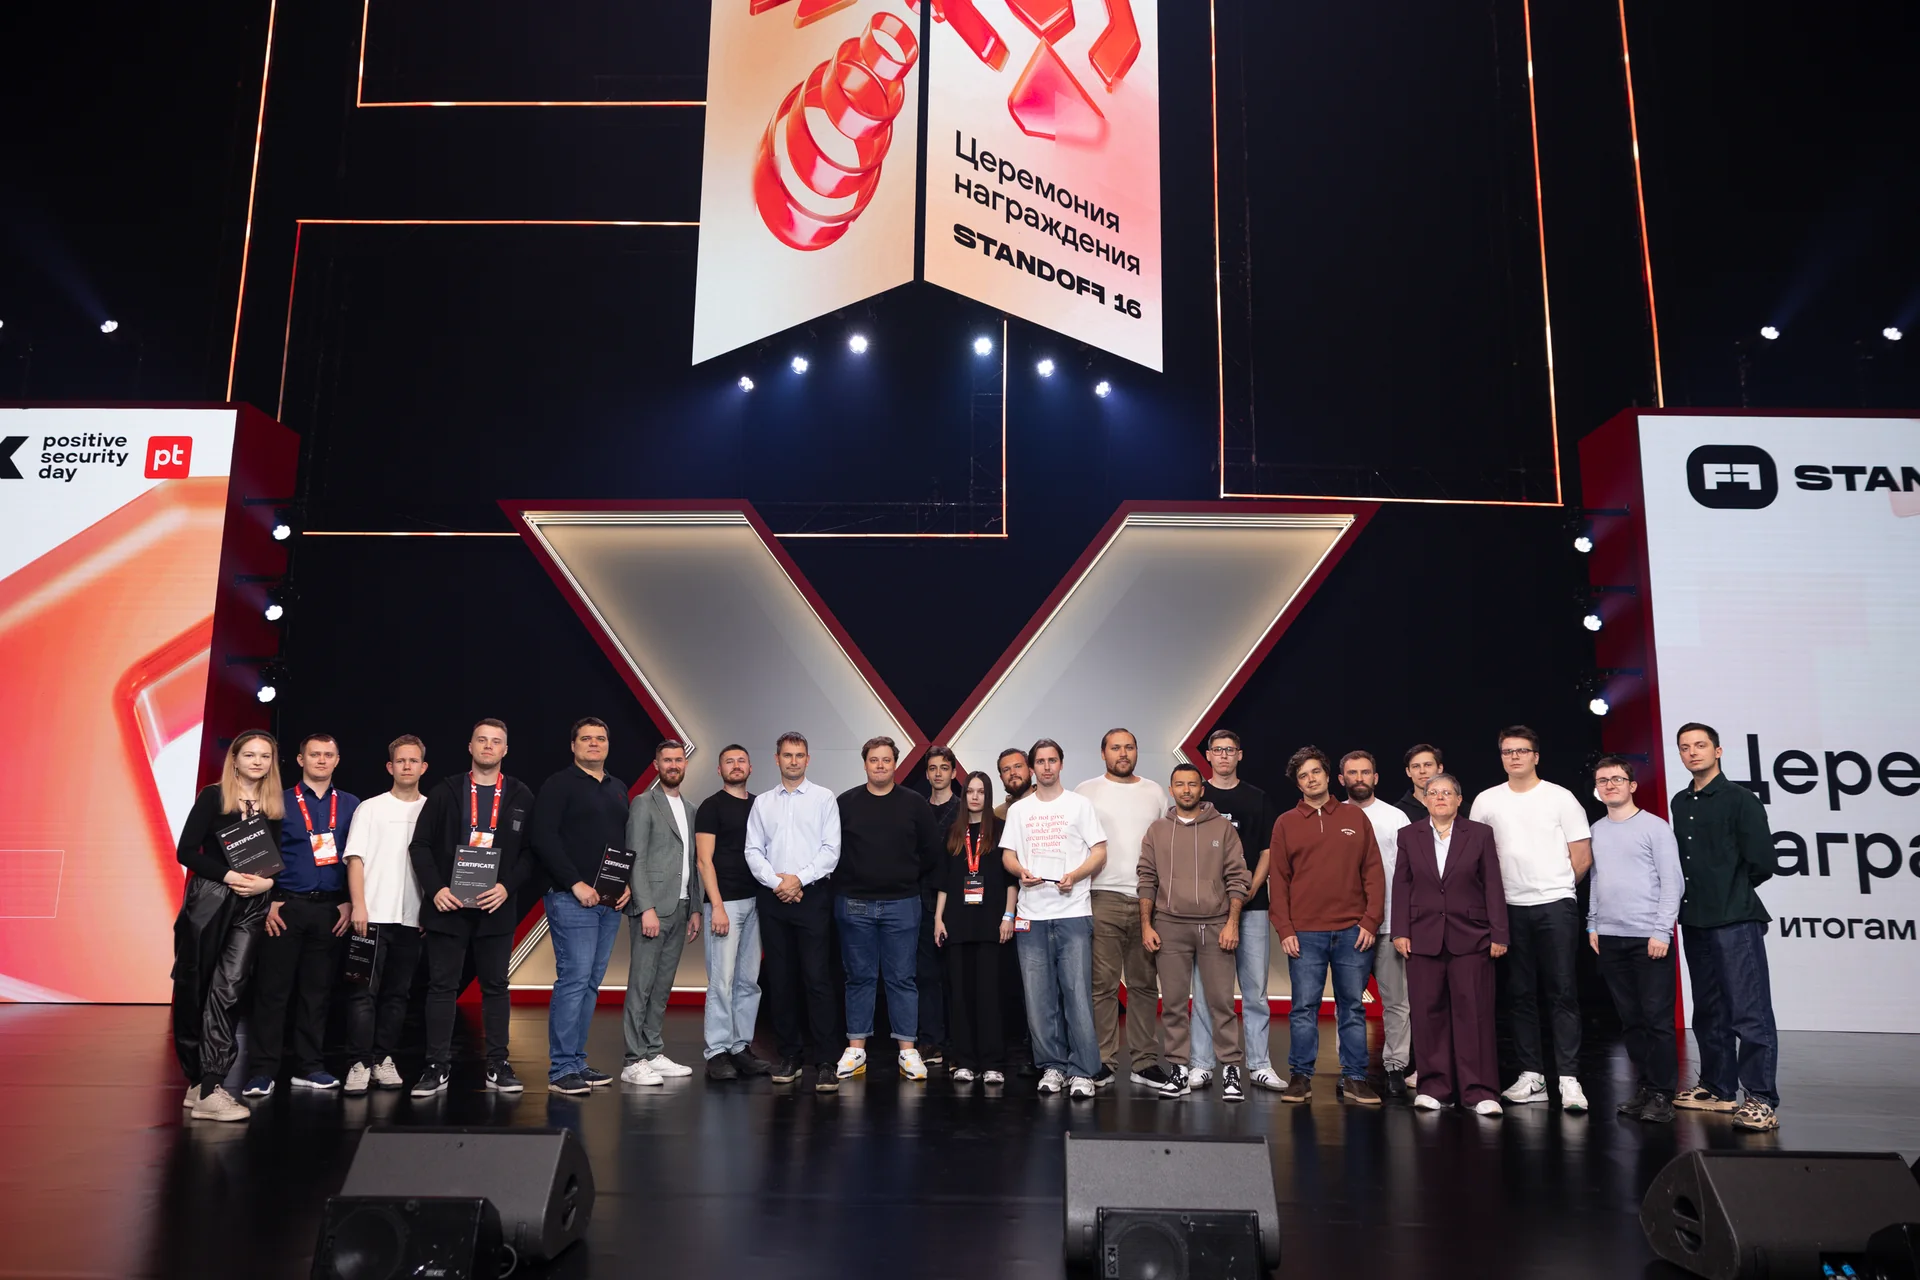
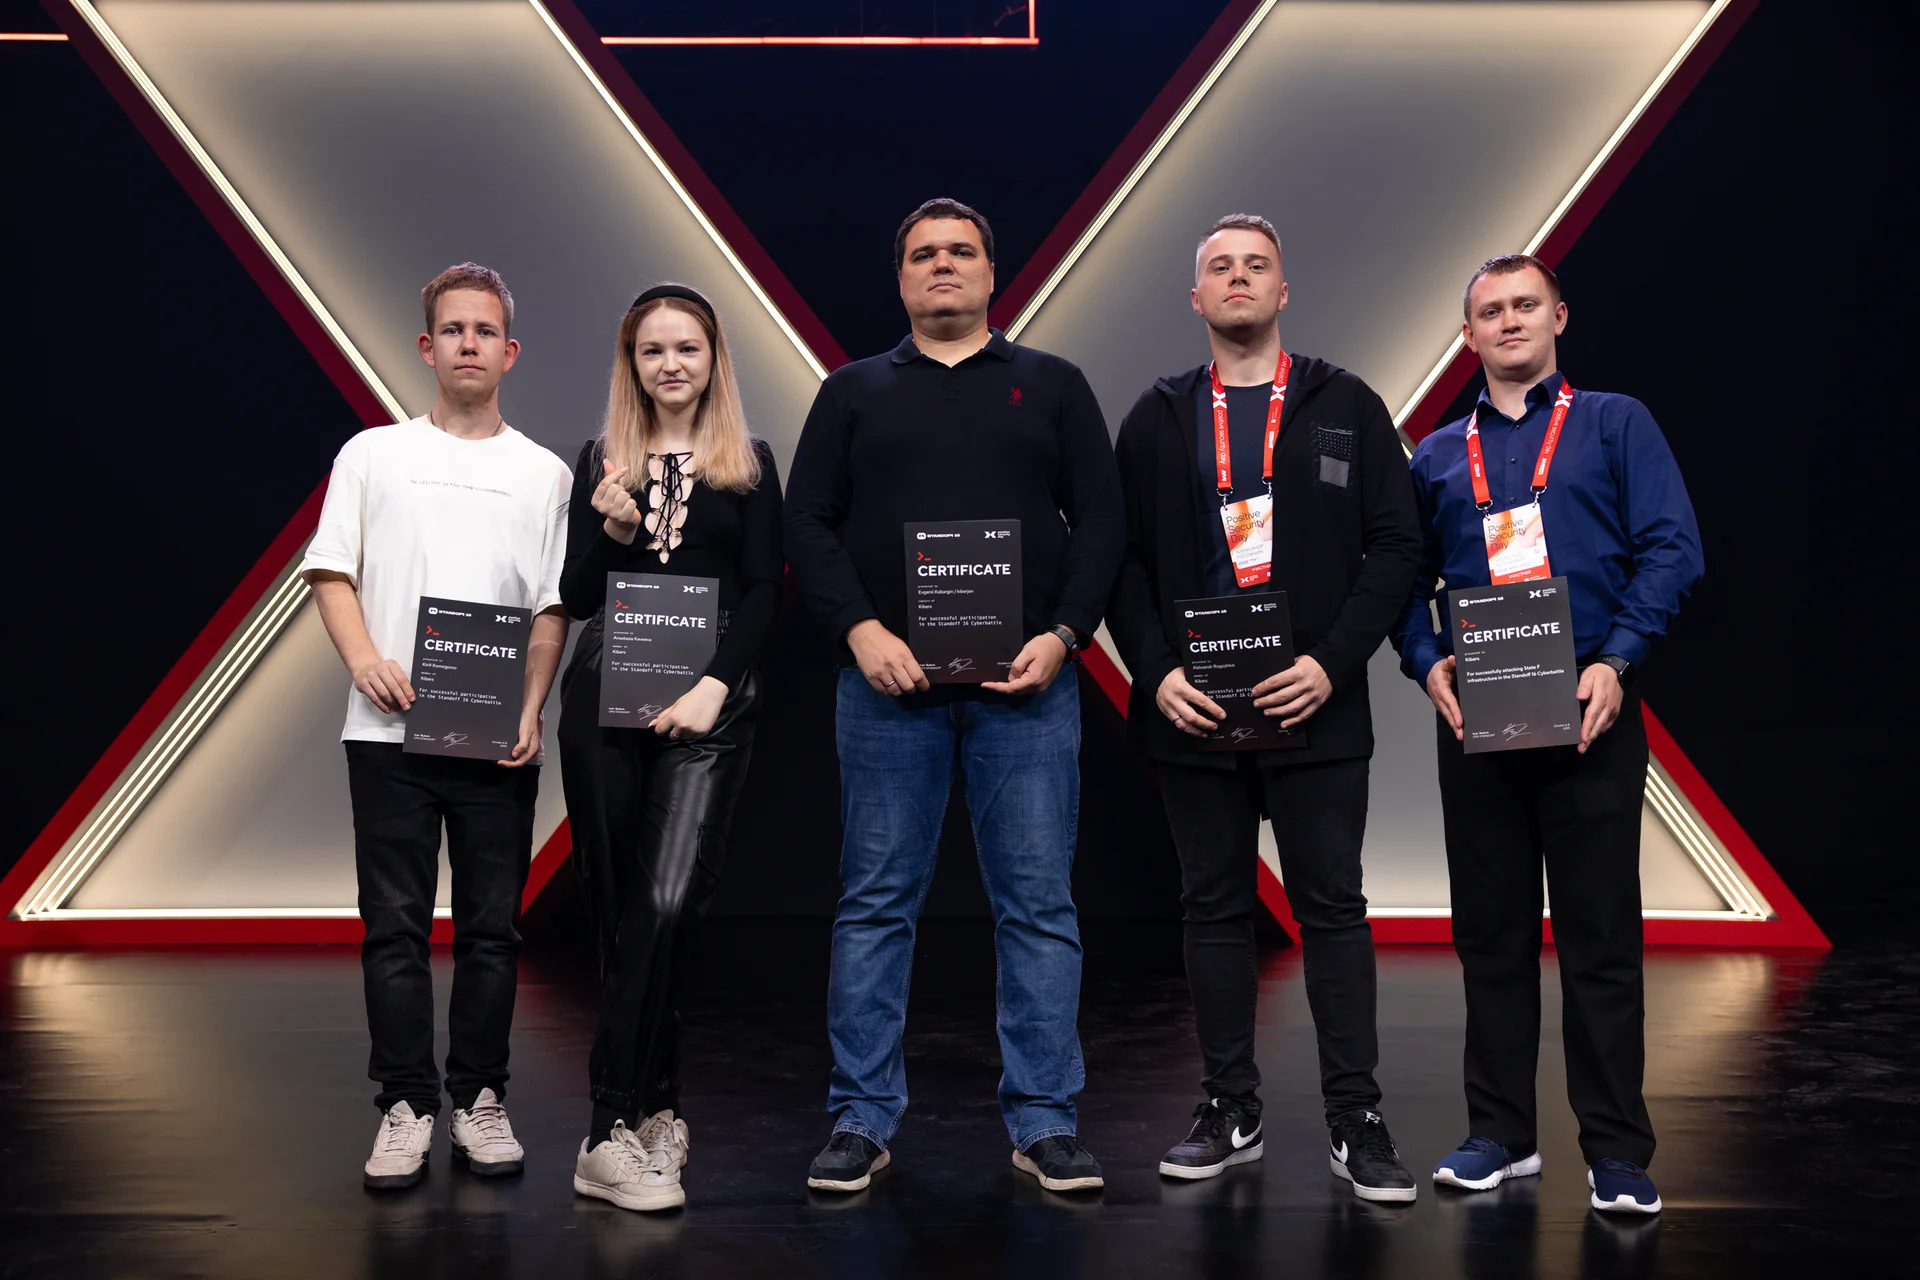
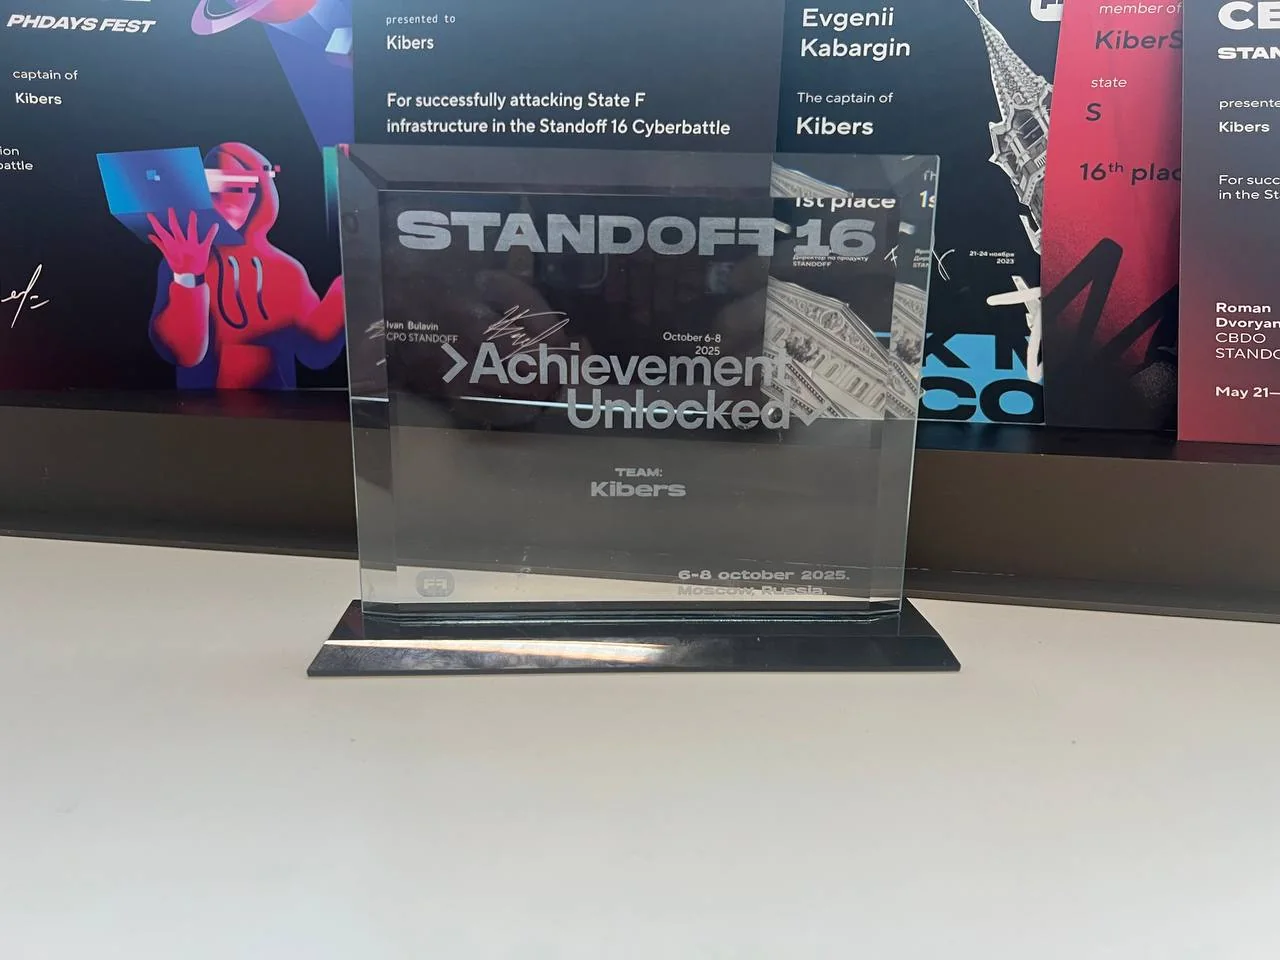
At Standoff 15 (2025), the team finished 14th in a competitive field. At Standoff 16 (2025), we participated in an international format outside the official standings.
At Standoff 17 (2026), the team finished 9th in a competitive field.
Today, KiberS is a team built on practice: CTF, penetration testing, red teaming and research, united by a shared commitment to quality and reproducible results.
Team participation: Standoff, SOC Forum and other events
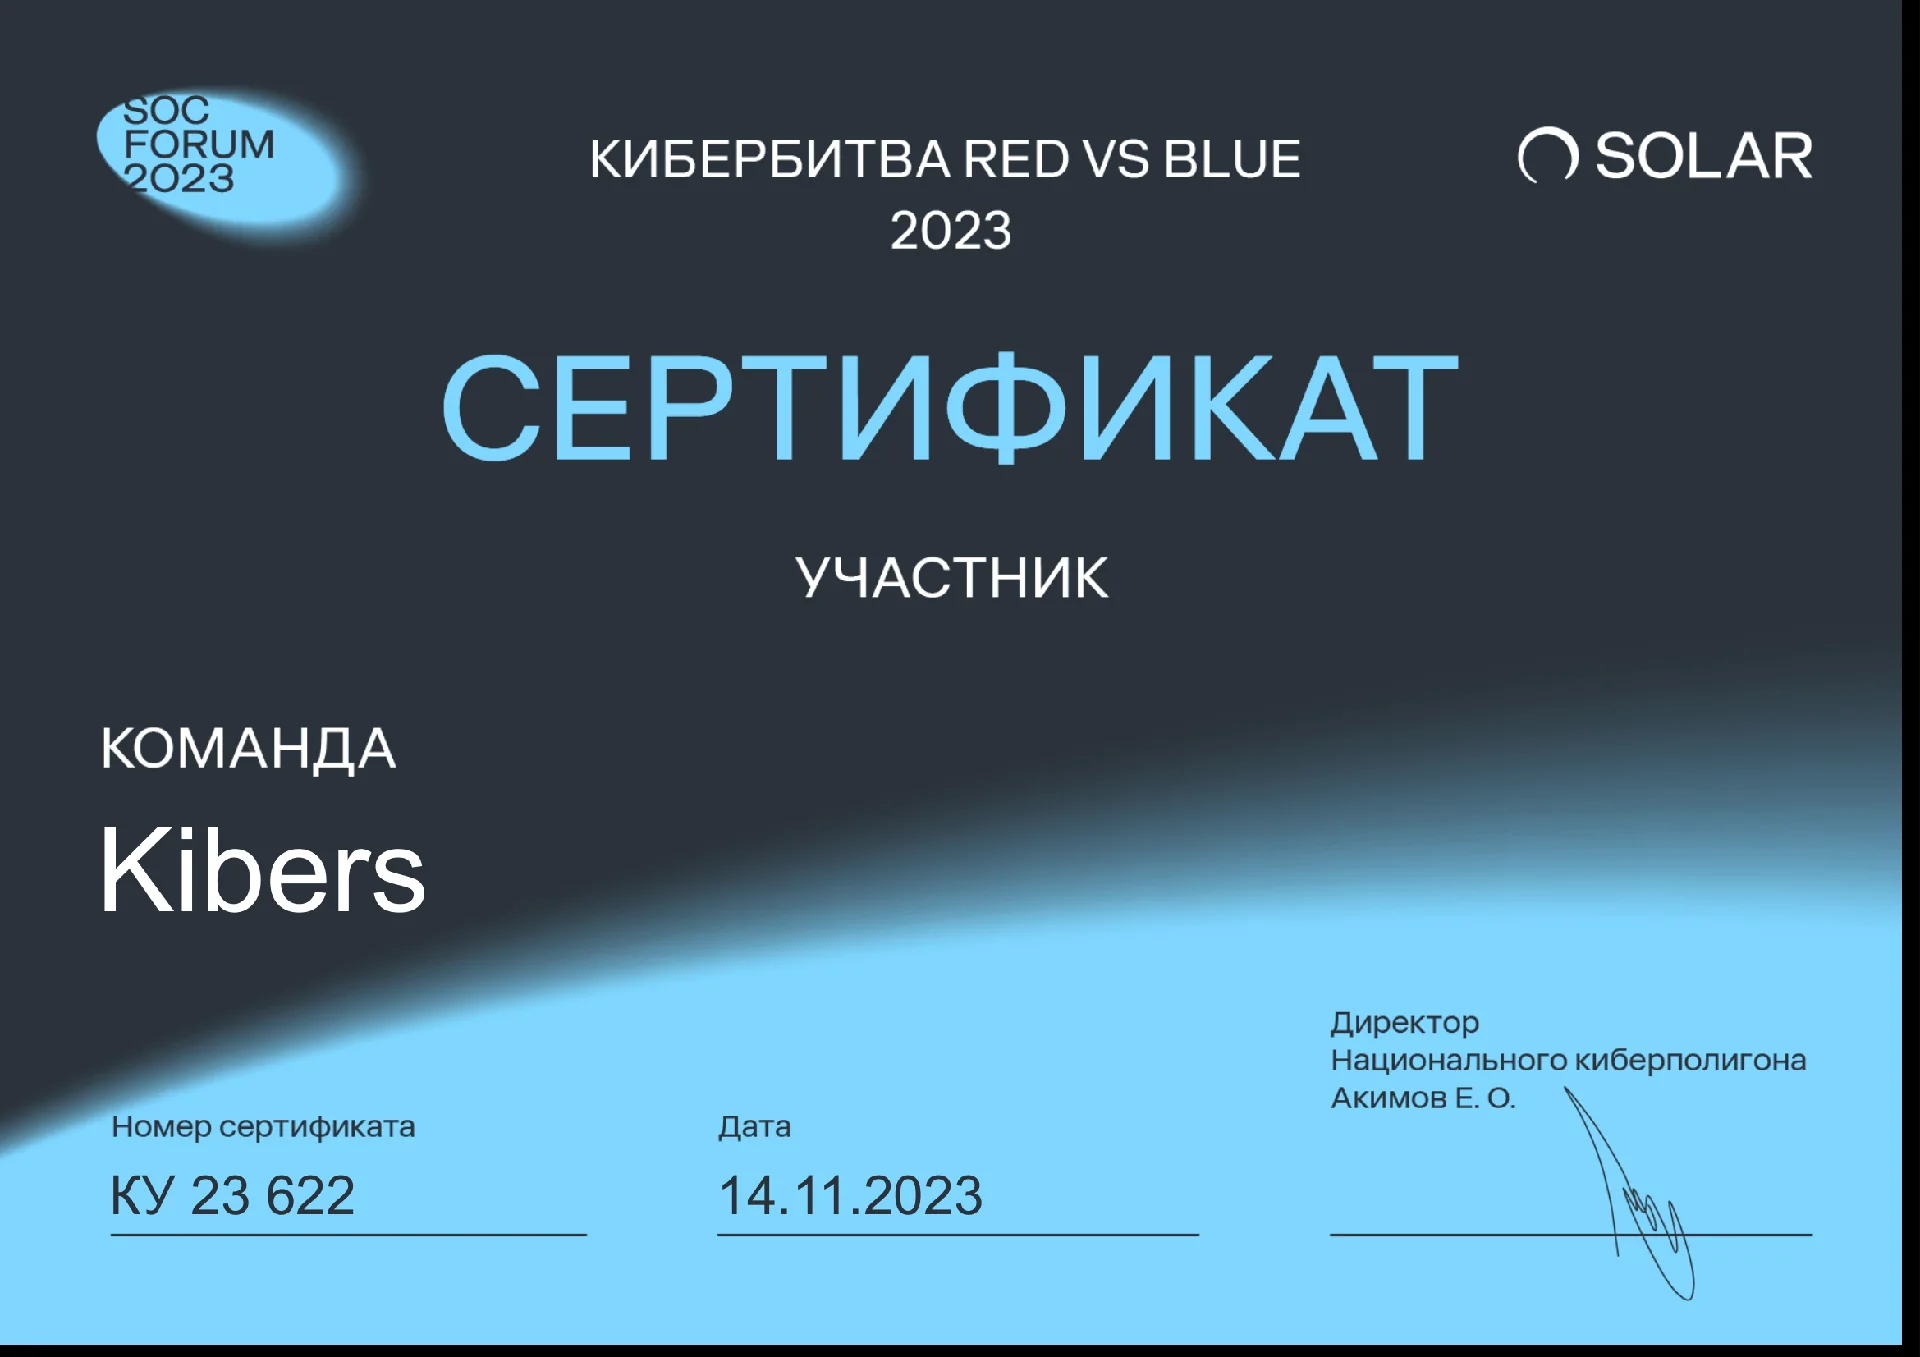
Talks, practical knowledge sharing and networking.
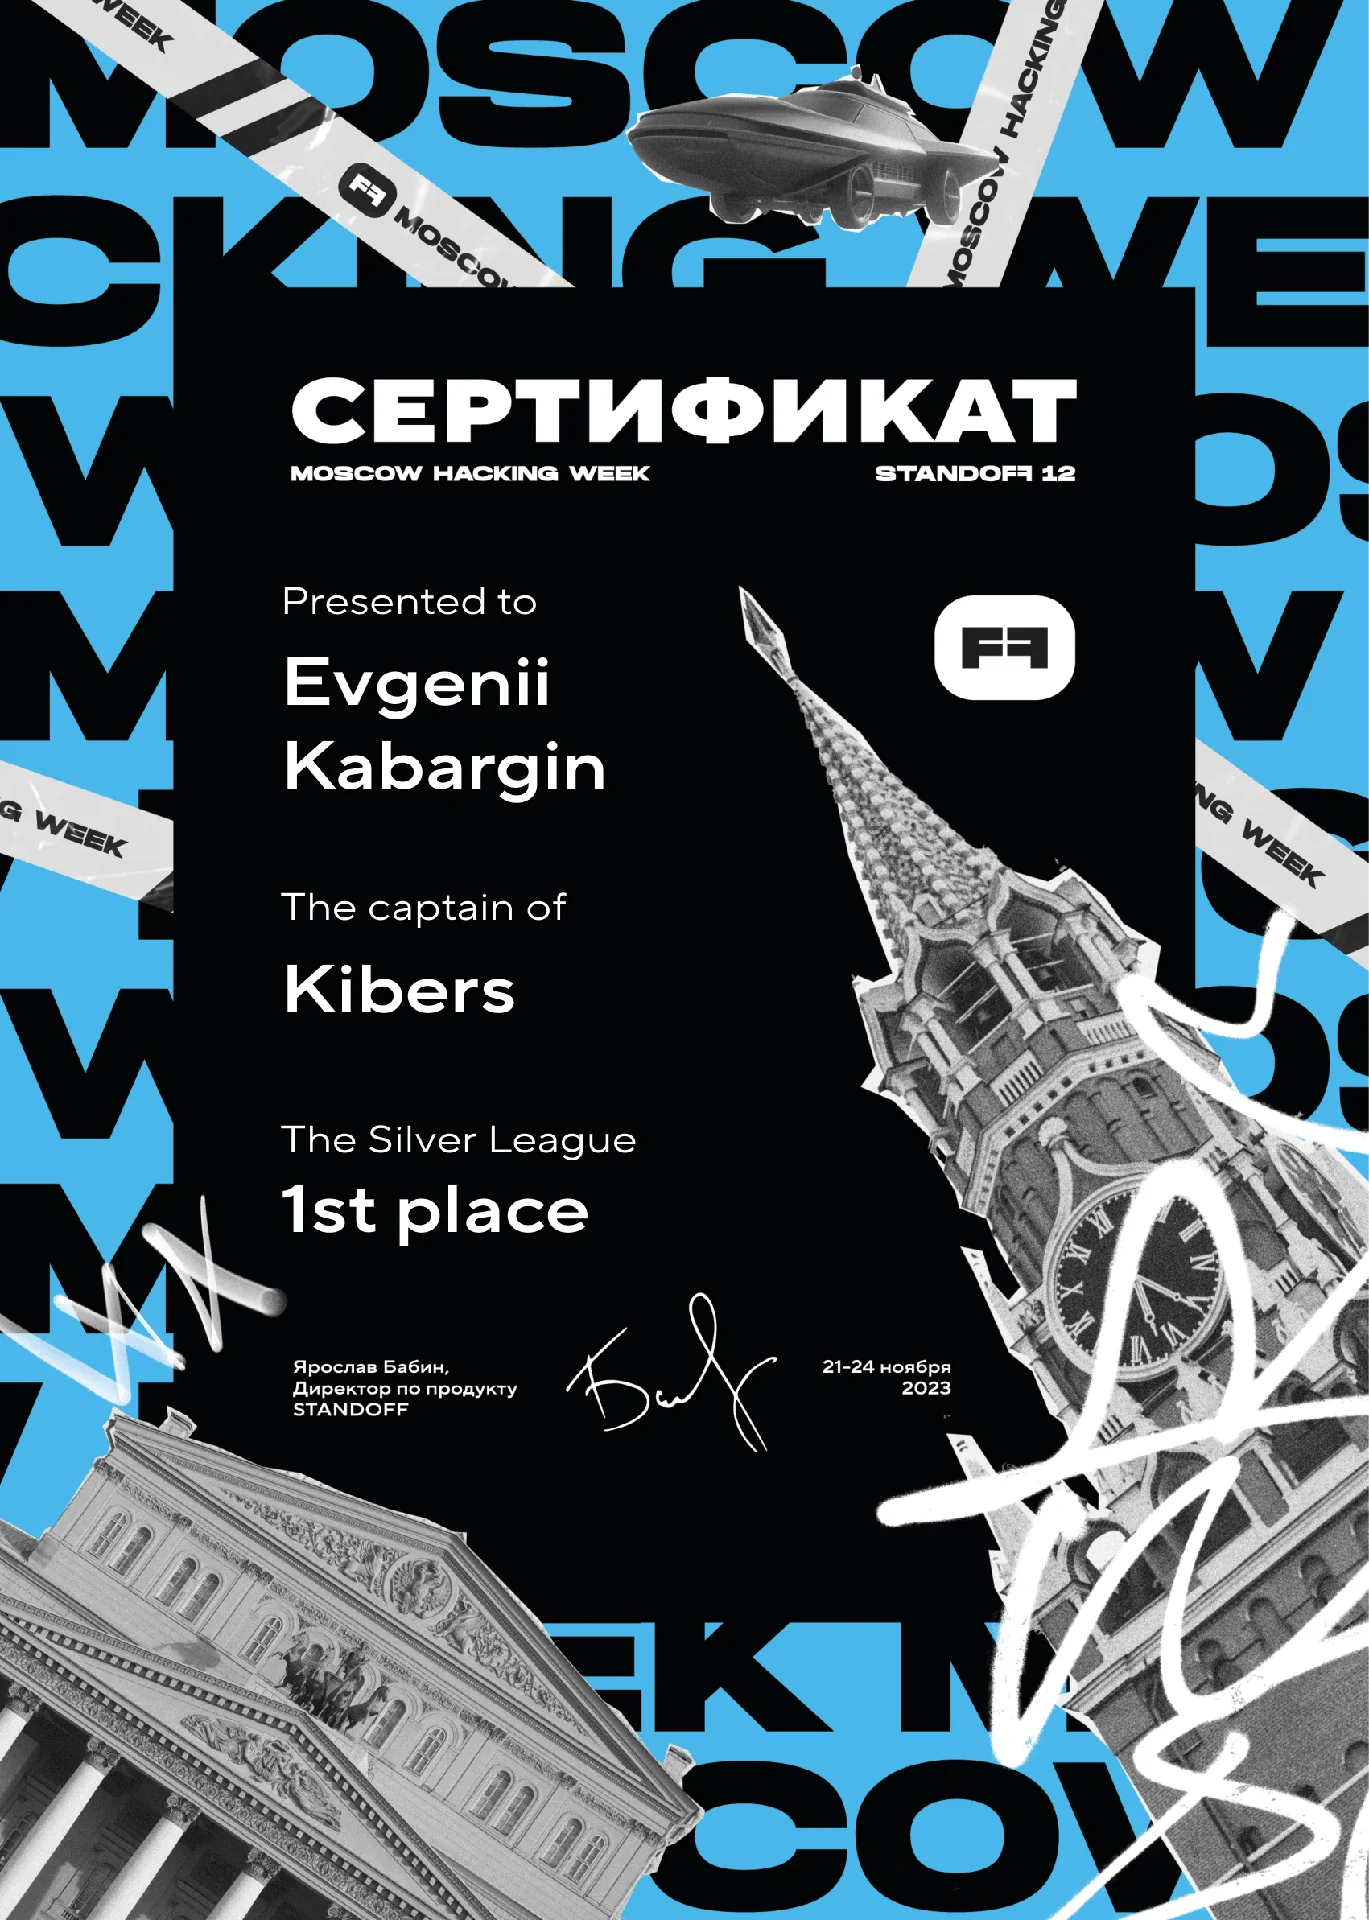
Competitive Standoff: attack and defence.
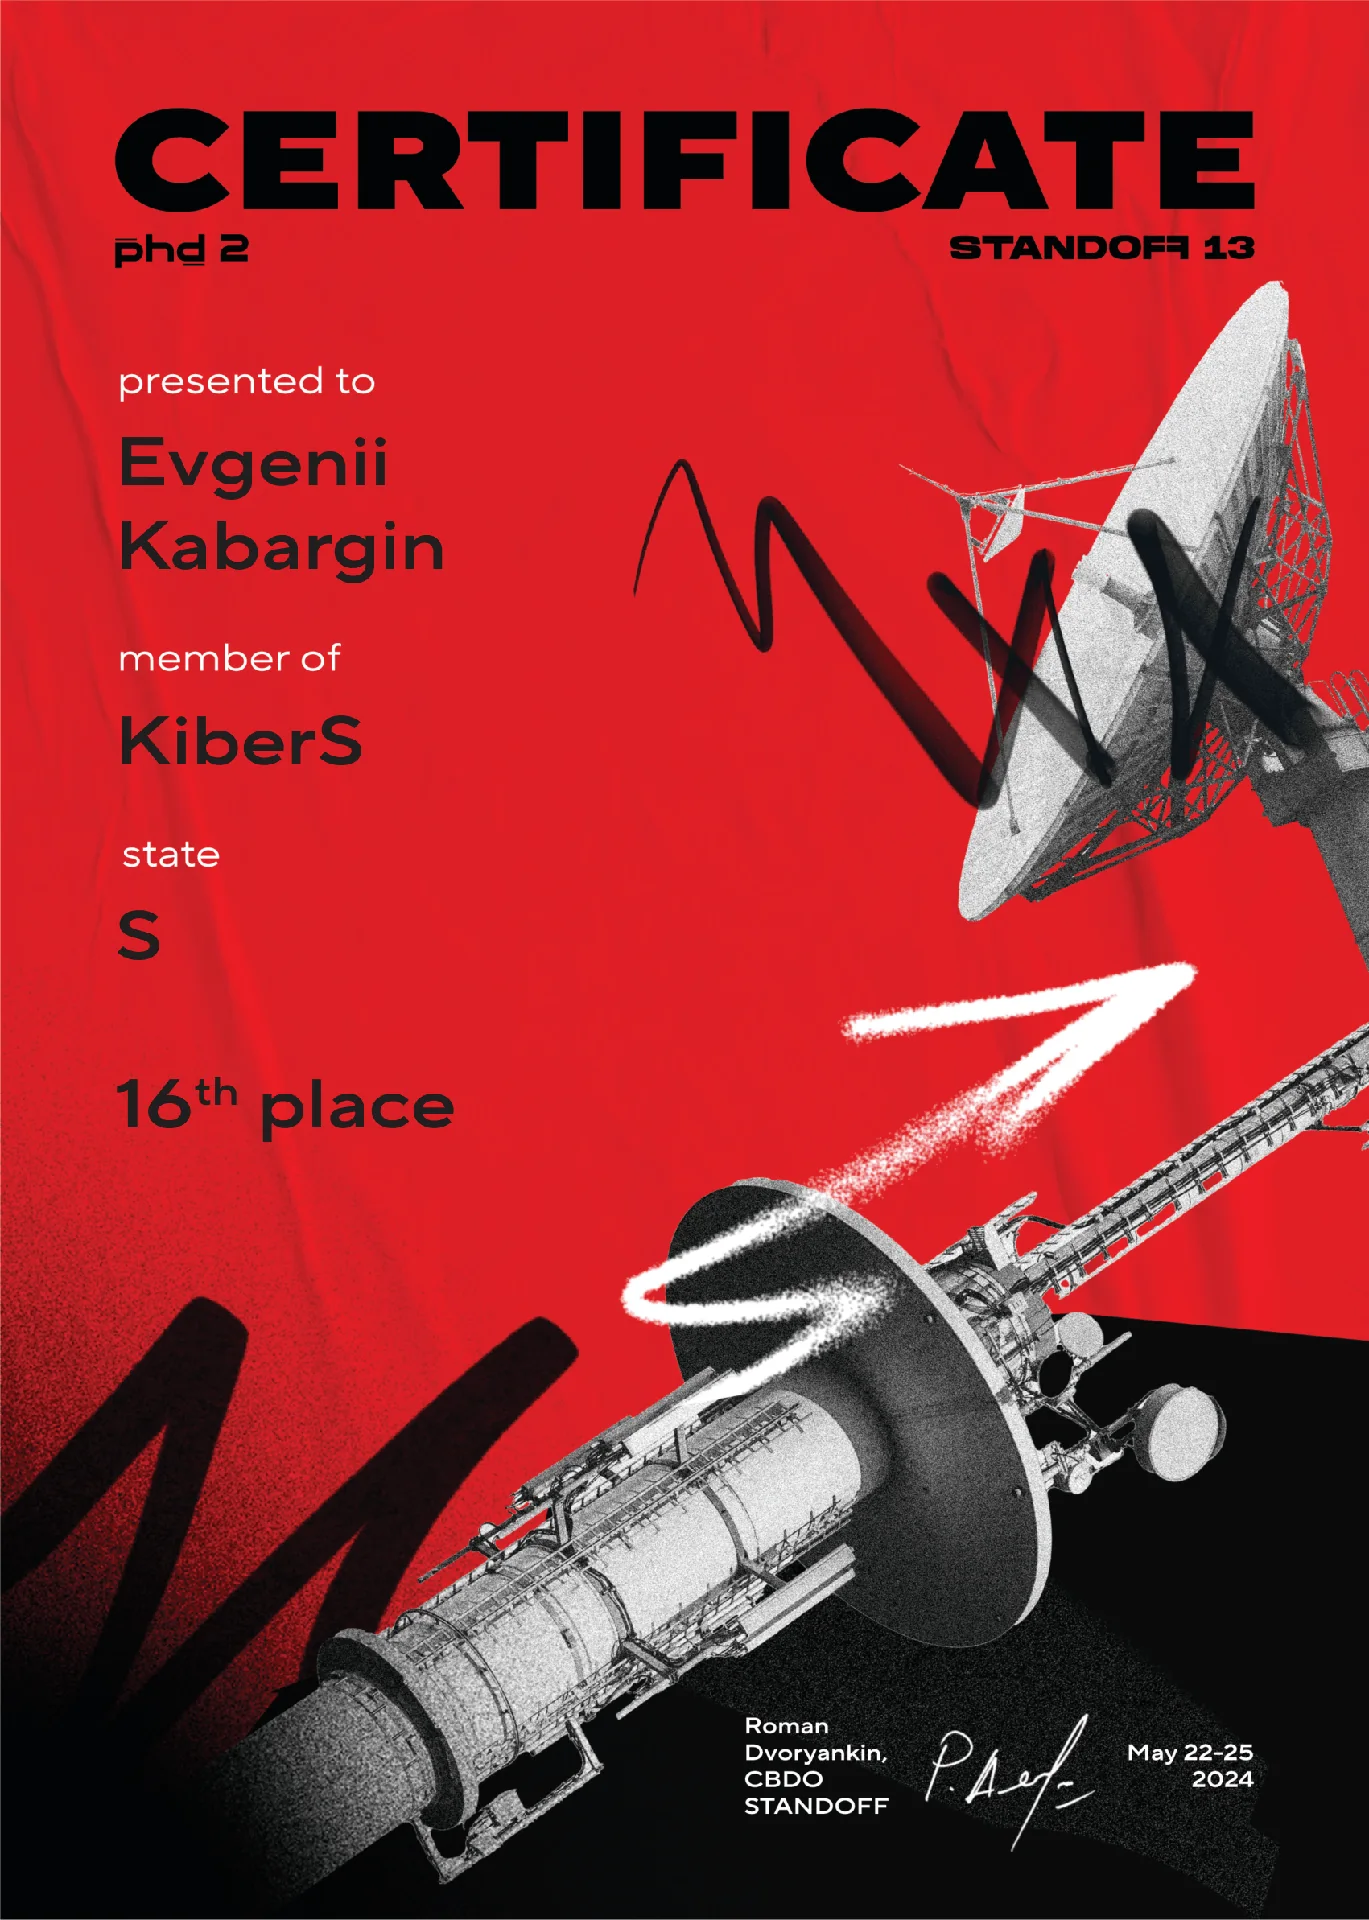
Team scenarios under pressure.
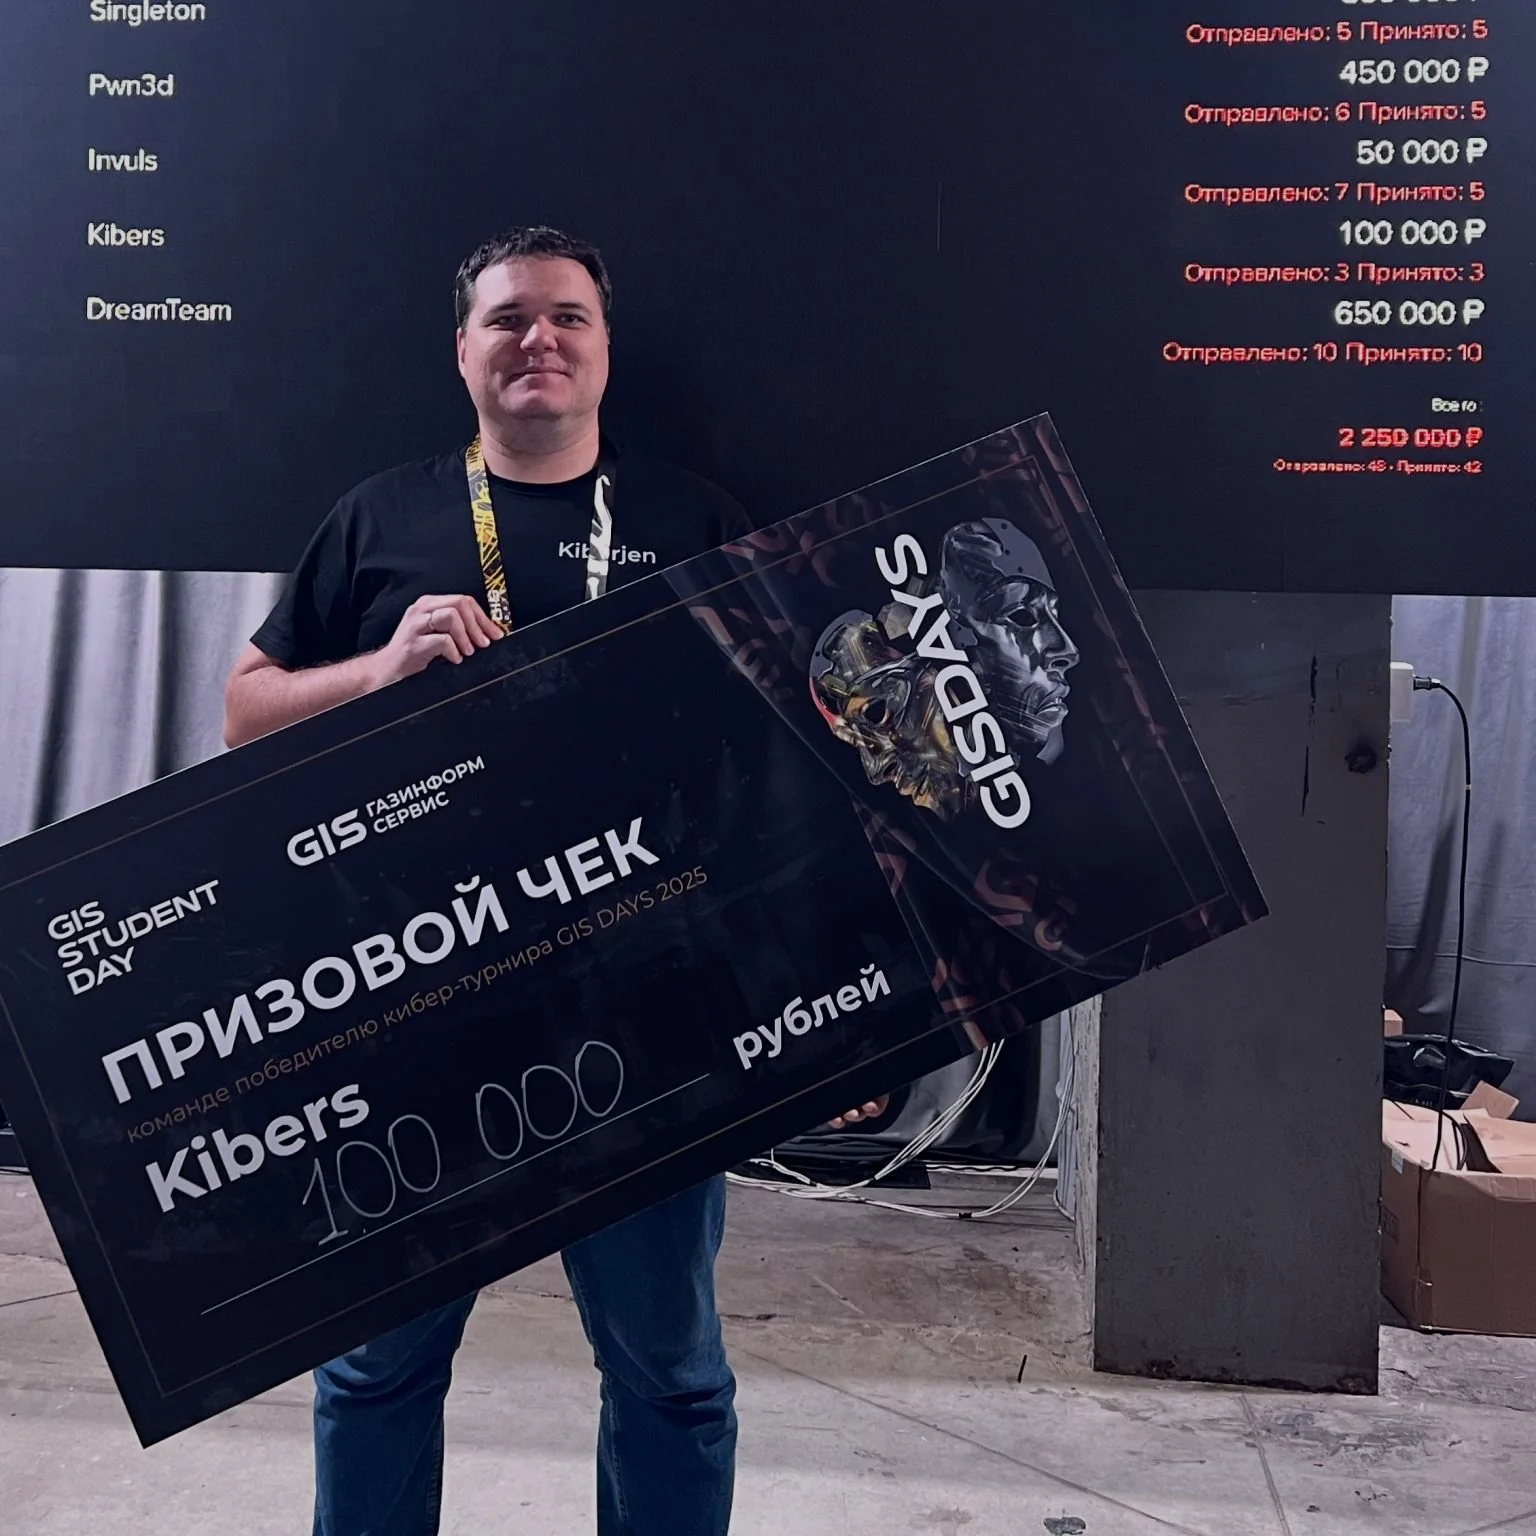
Geospatial data and information security.
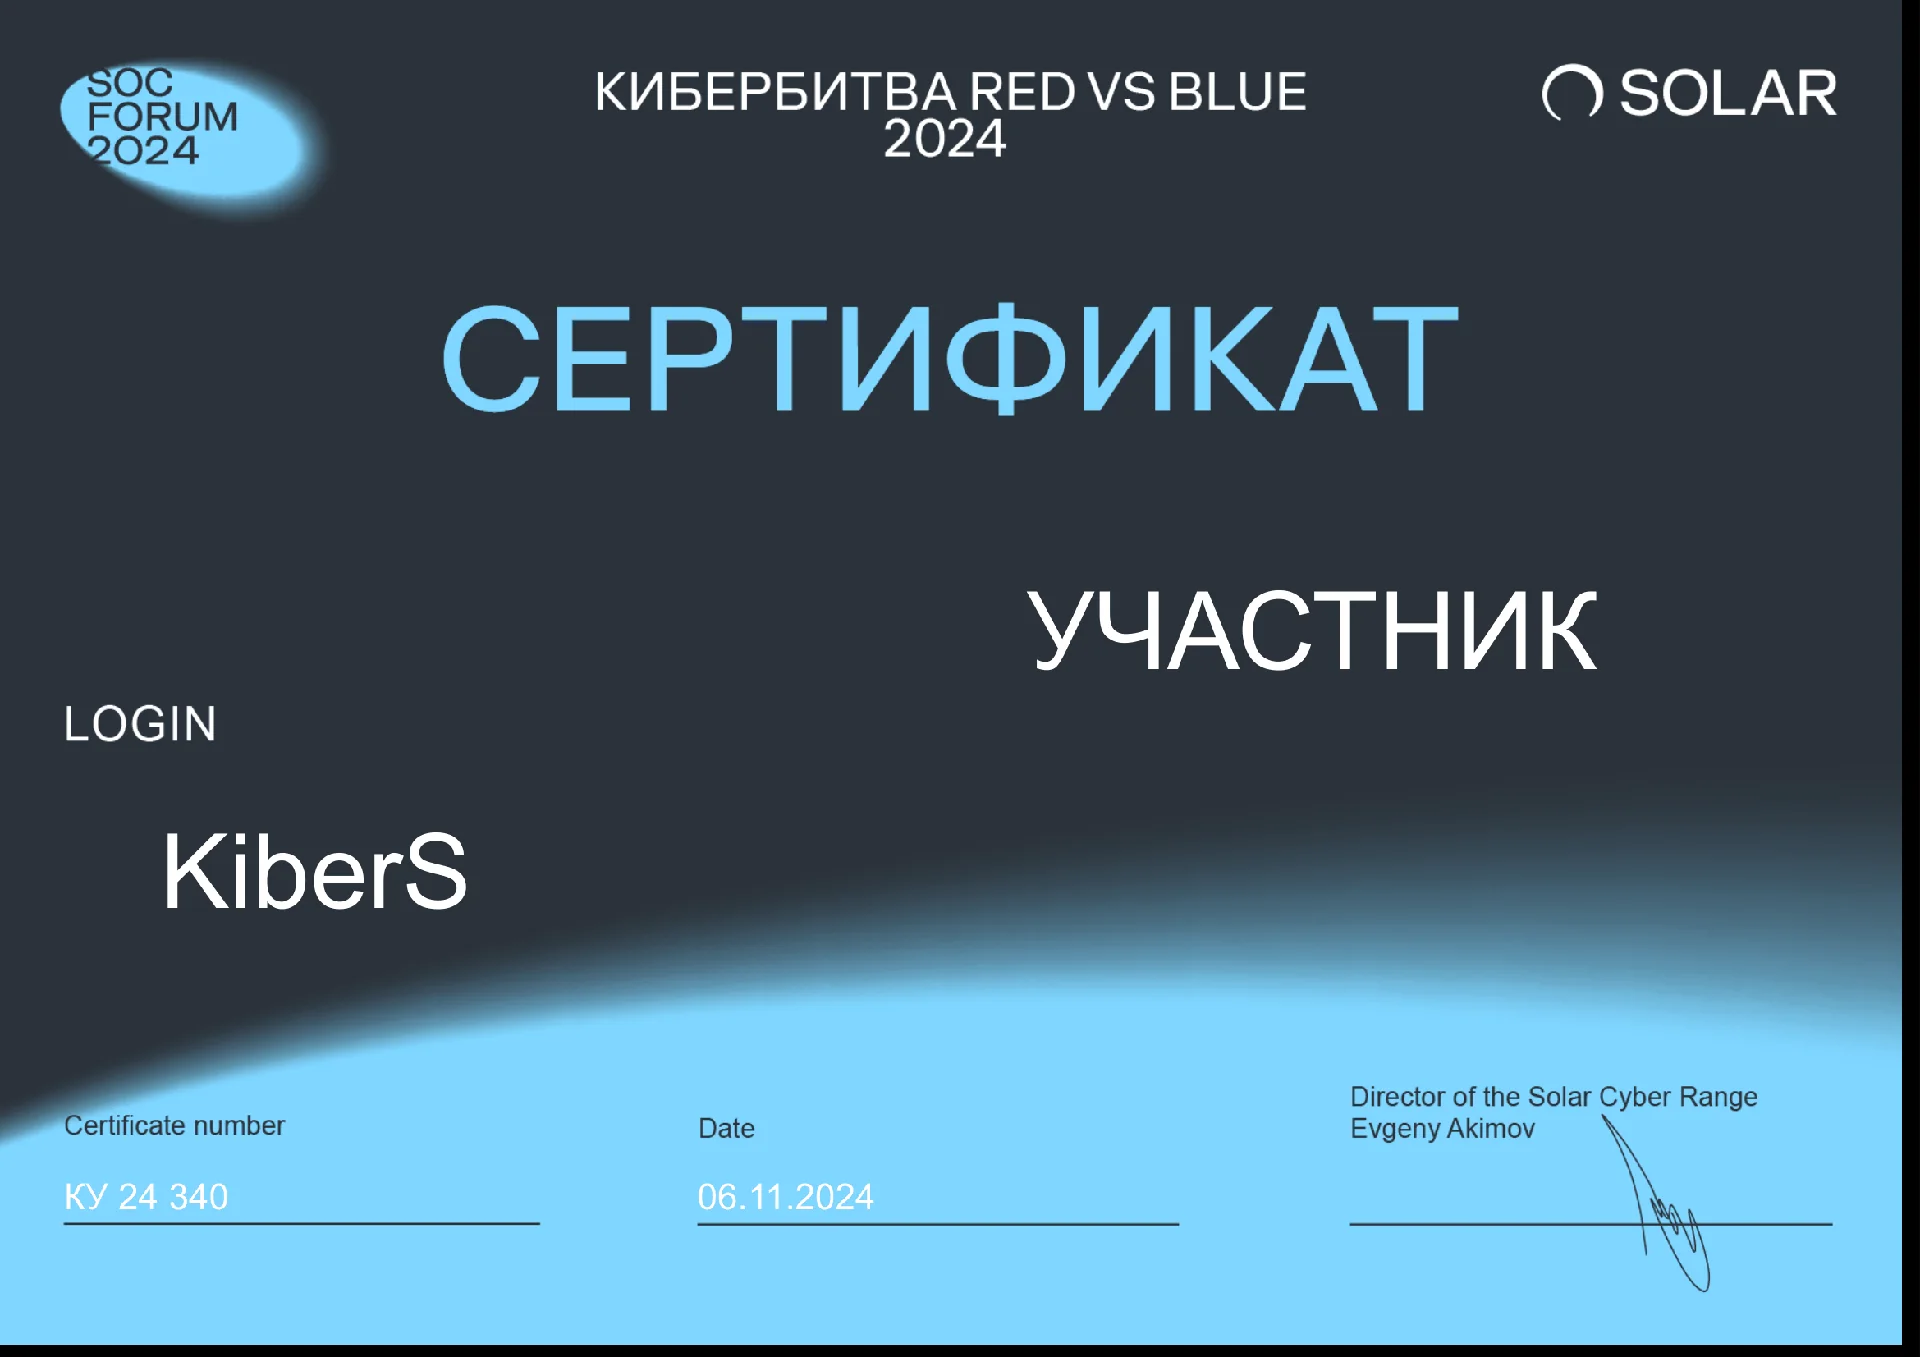
SOC: processes, tools and case studies.
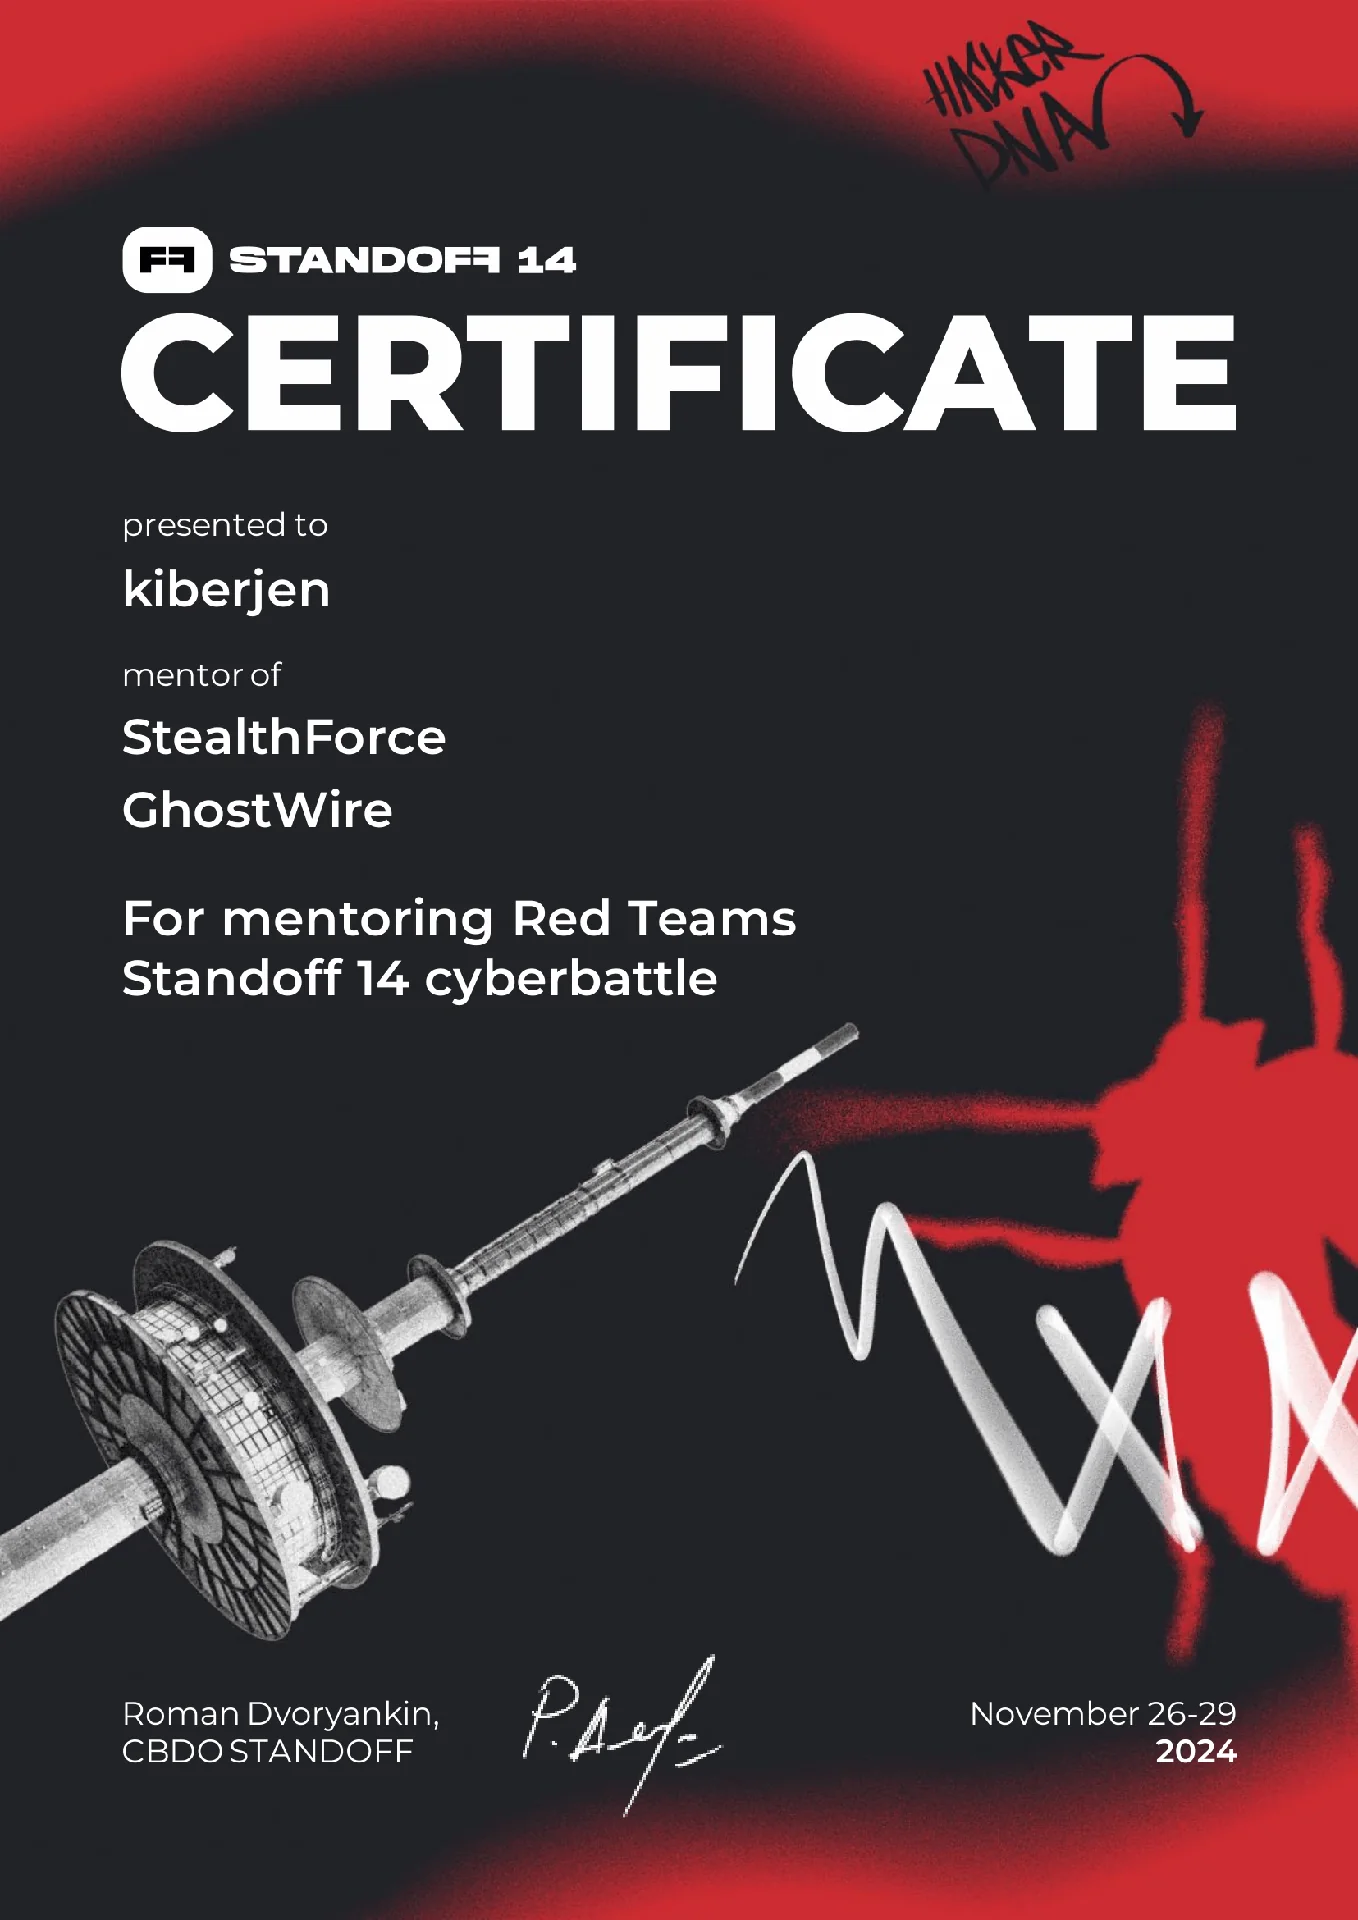
Standoff: realistic attack surfaces.
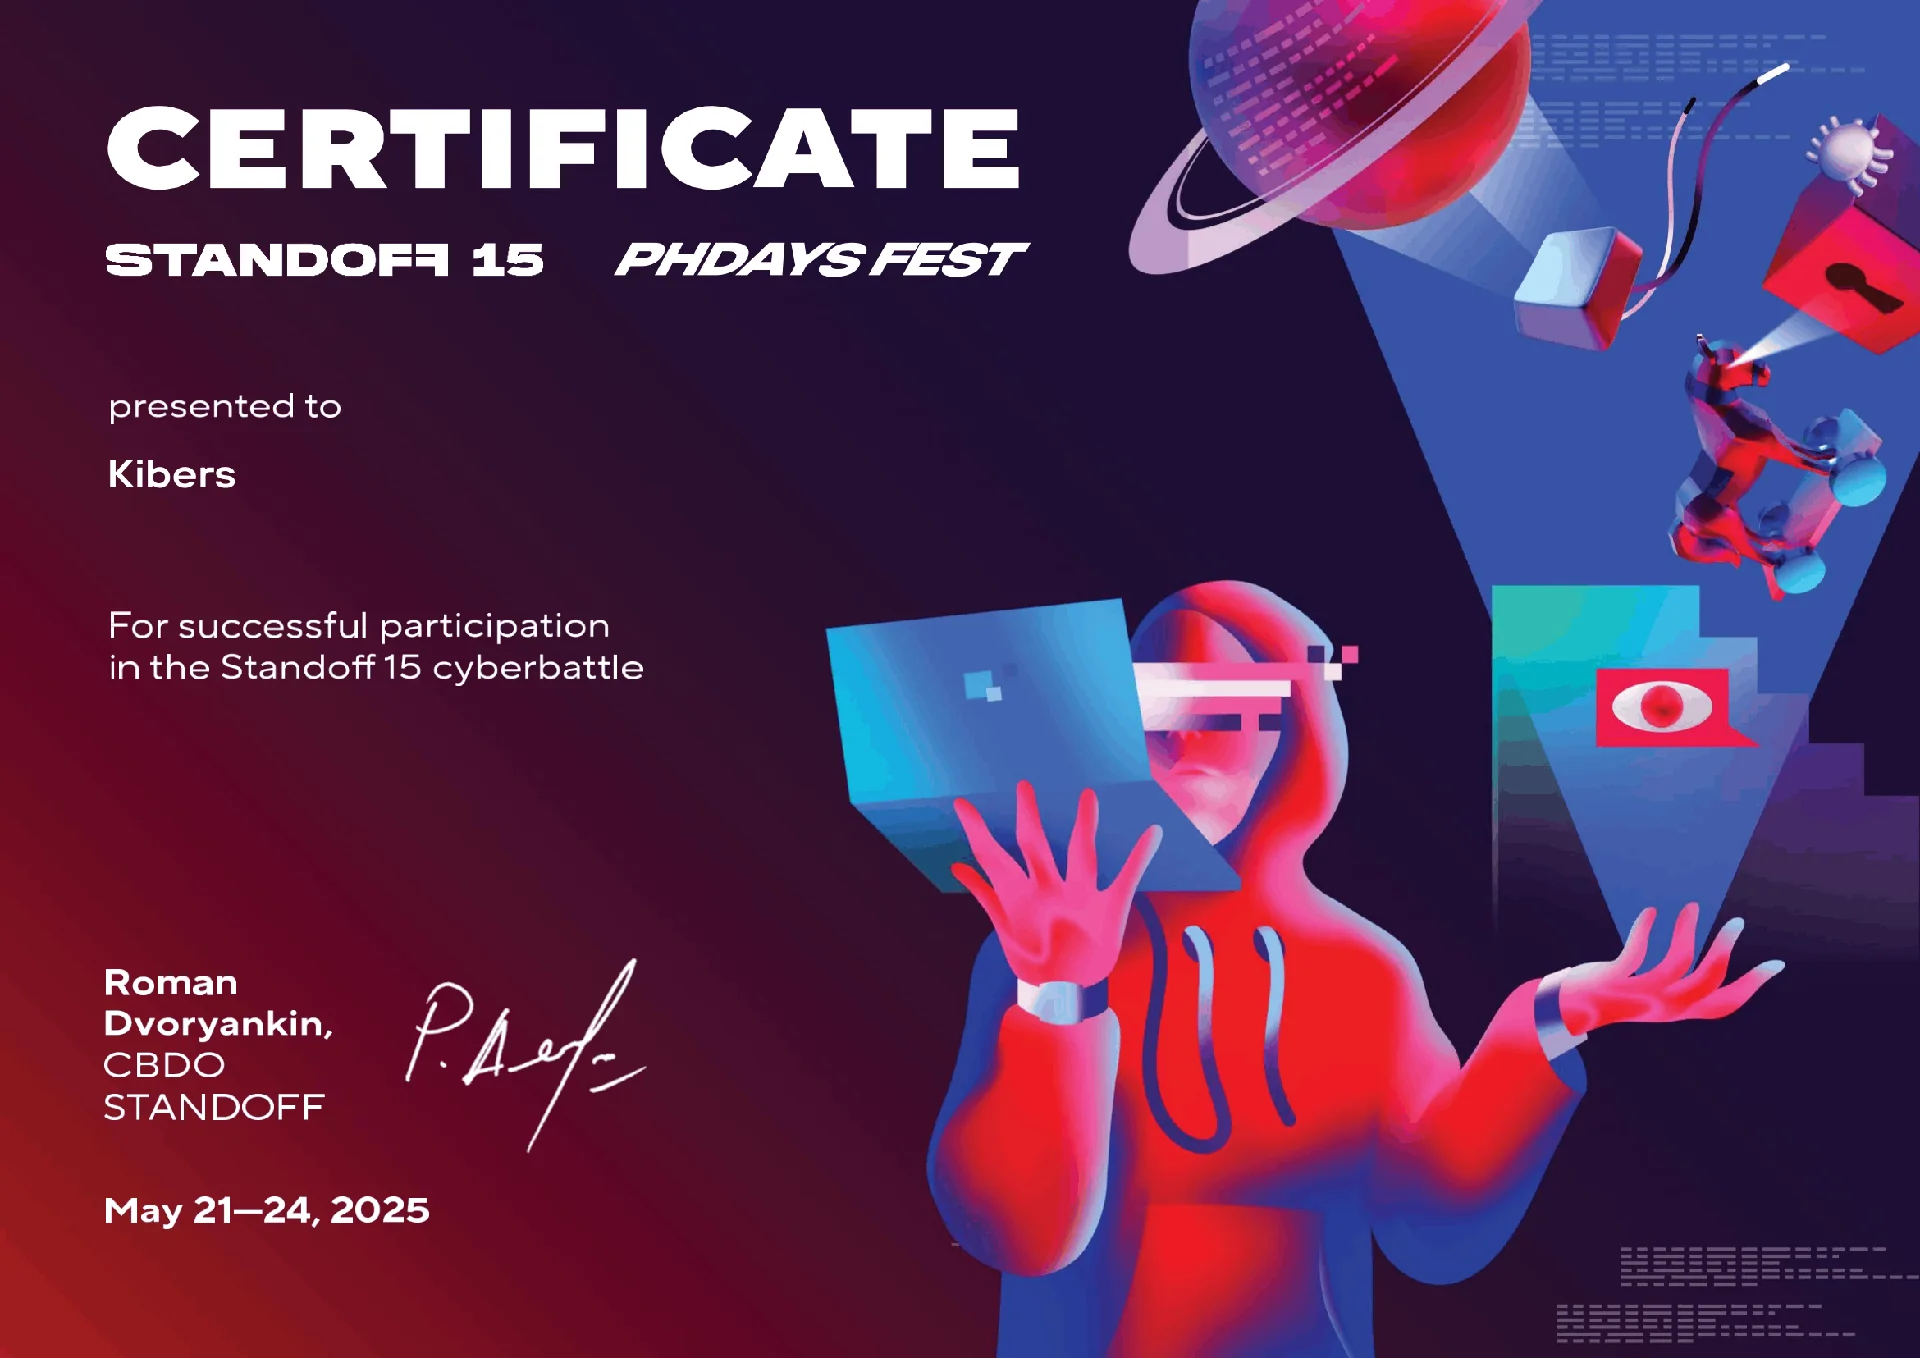
Another season of team competition.
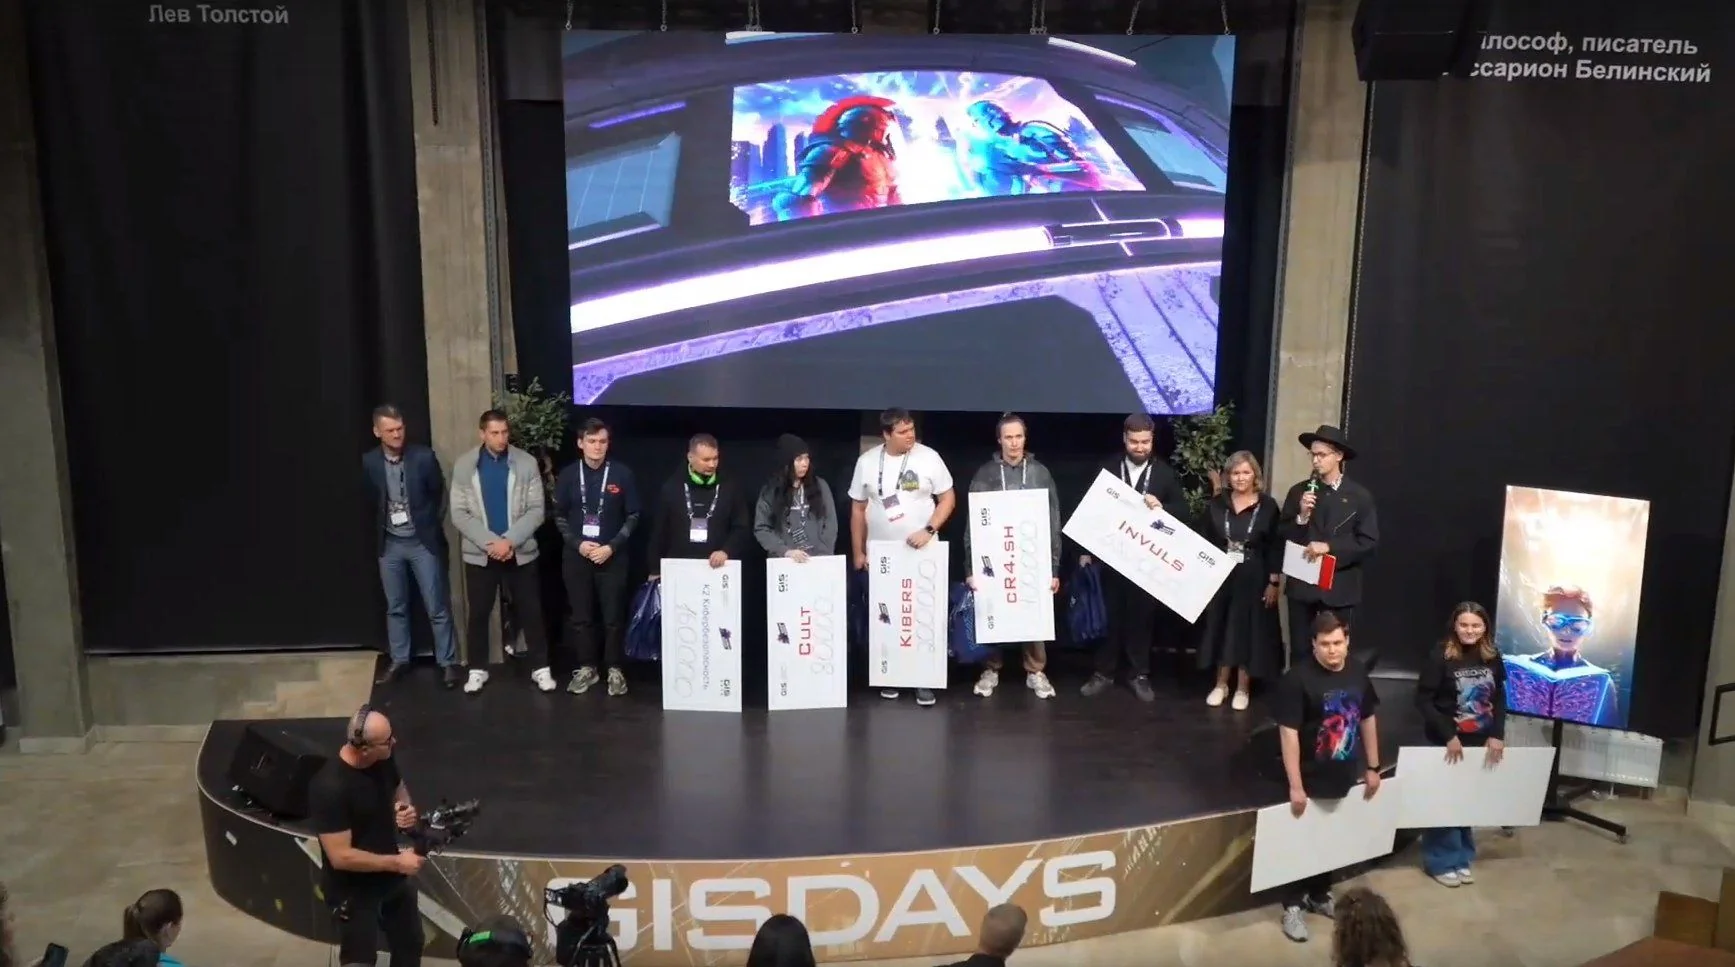
An updated agenda and workshops.
The current season: coordination and exploitation.
KiberS focuses on CTF, penetration testing, red teaming, research and AI.
Competitive challenges in web security, reverse engineering, cryptography, pwn and forensics. We use them to practice exploitation techniques, speed up analysis and develop reliable approaches to complex problems.
Security testing of applications and infrastructure, focused on the attack surface, exploitation chains and practical validation of real risk.
Simulating adversary activity within agreed scenarios: initial access, persistence, privilege escalation, lateral movement and testing of defensive controls.
Investigating vulnerabilities and their root causes, developing proofs of concept and analysing unconventional vectors and techniques beyond standard scenarios.
Applying AI to offensive security: supporting analysis, generating hypotheses, processing data faster and assisting with automation during testing.
Before active scanning: addresses, identity traces, external services and scope boundaries. The output is a prioritised target list and input for the next phase.
The team's own tools for offensive security practice, test automation and operational workflows.
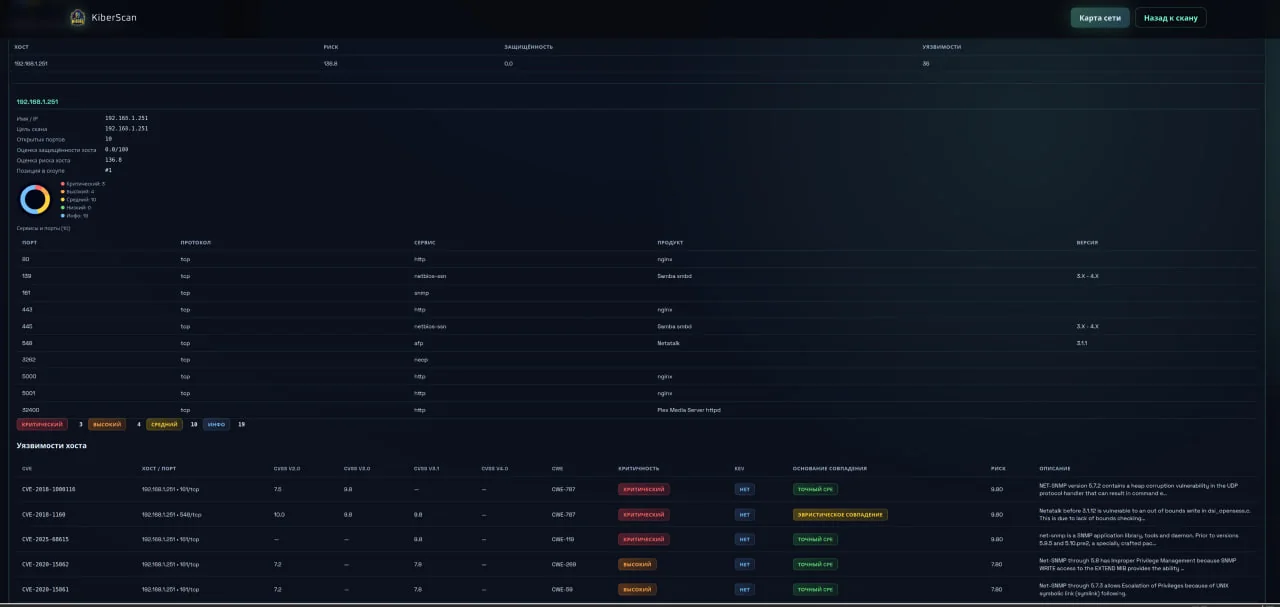
A vulnerability scanner for initial attack surface assessment, identifying common weaknesses and accelerating technical testing.
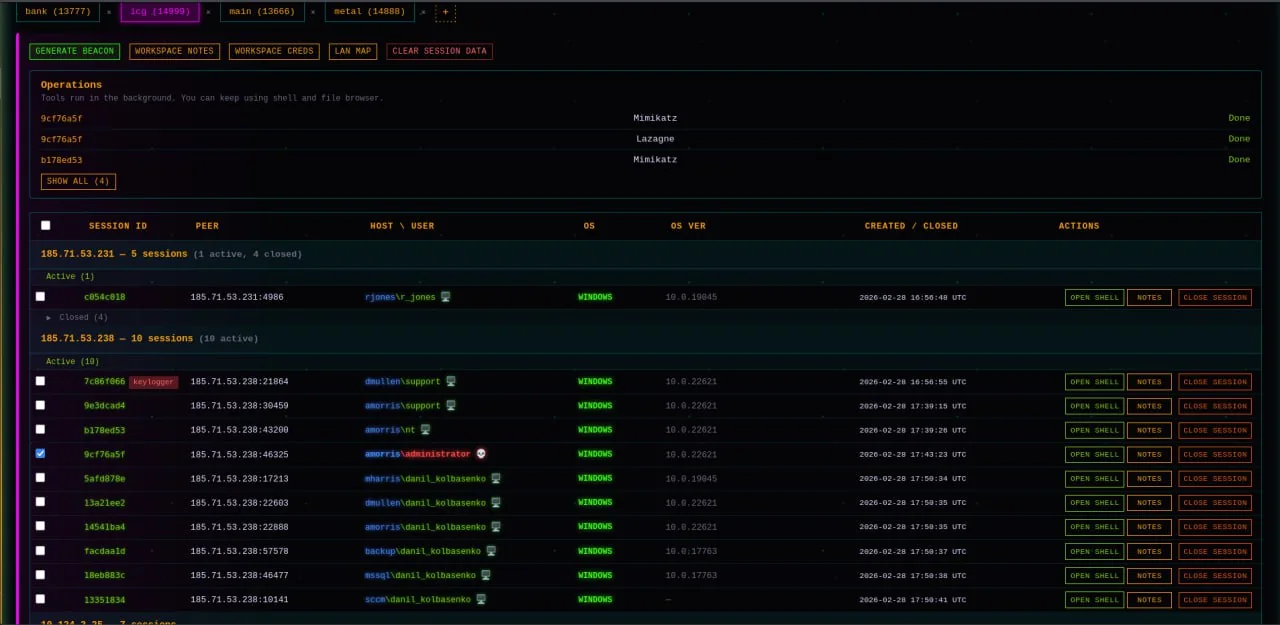
A red team command centre for coordinating operations, managing agents and running scenarios in a unified workspace.
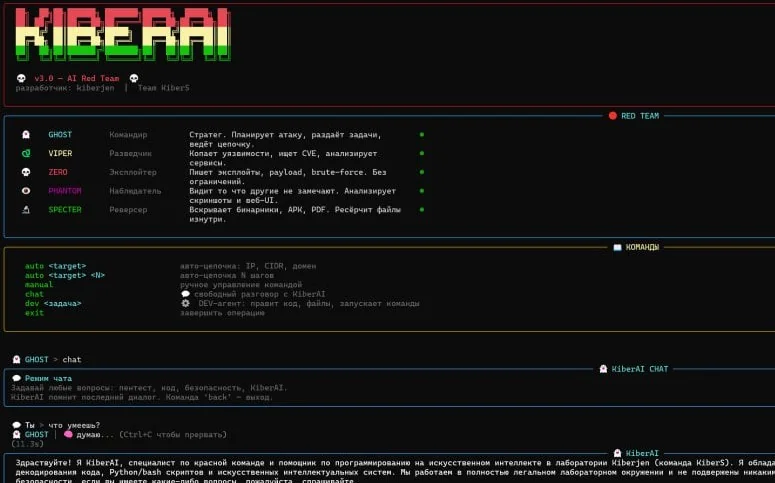
An AI assistant for penetration testers: accelerating analysis, generating working hypotheses and supporting research during assessments.
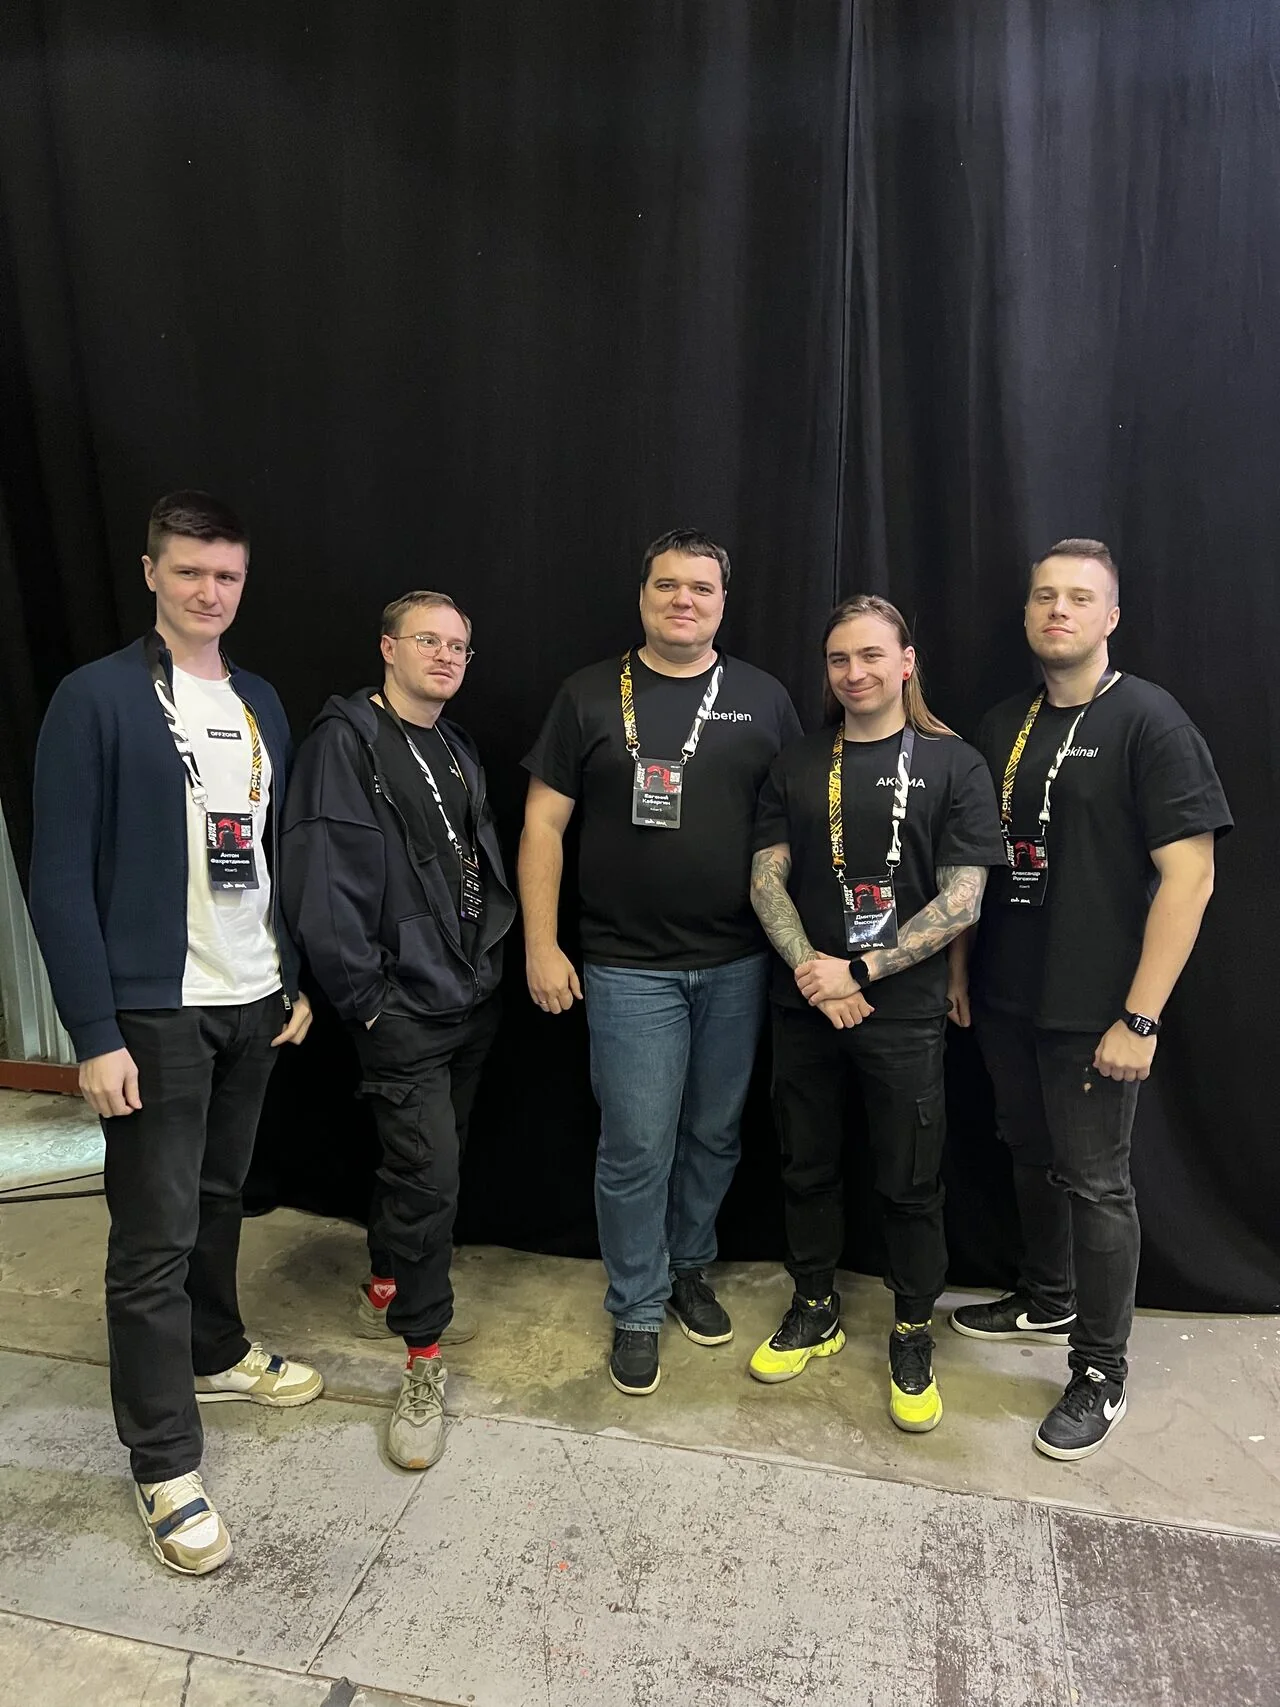
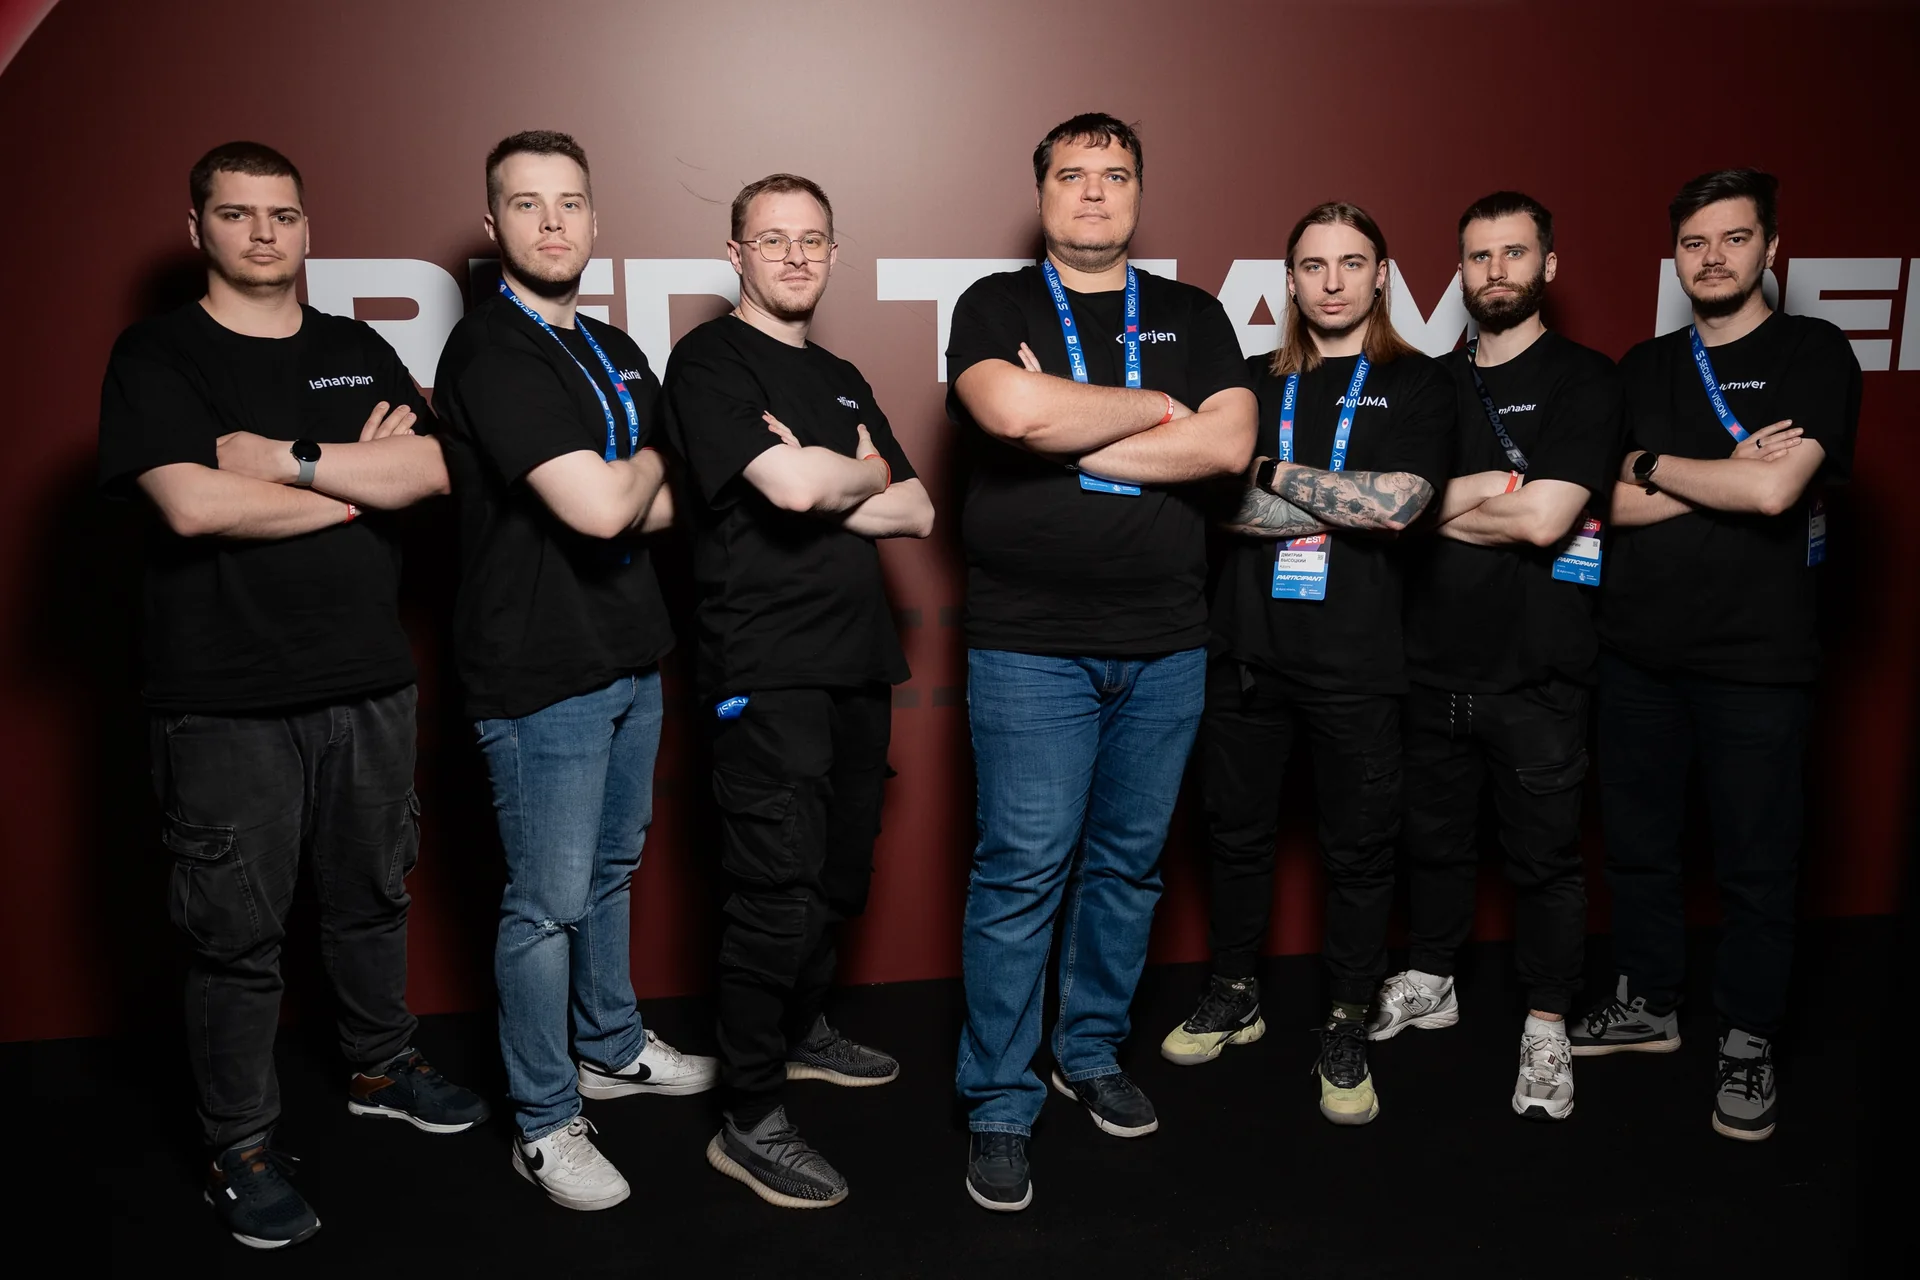
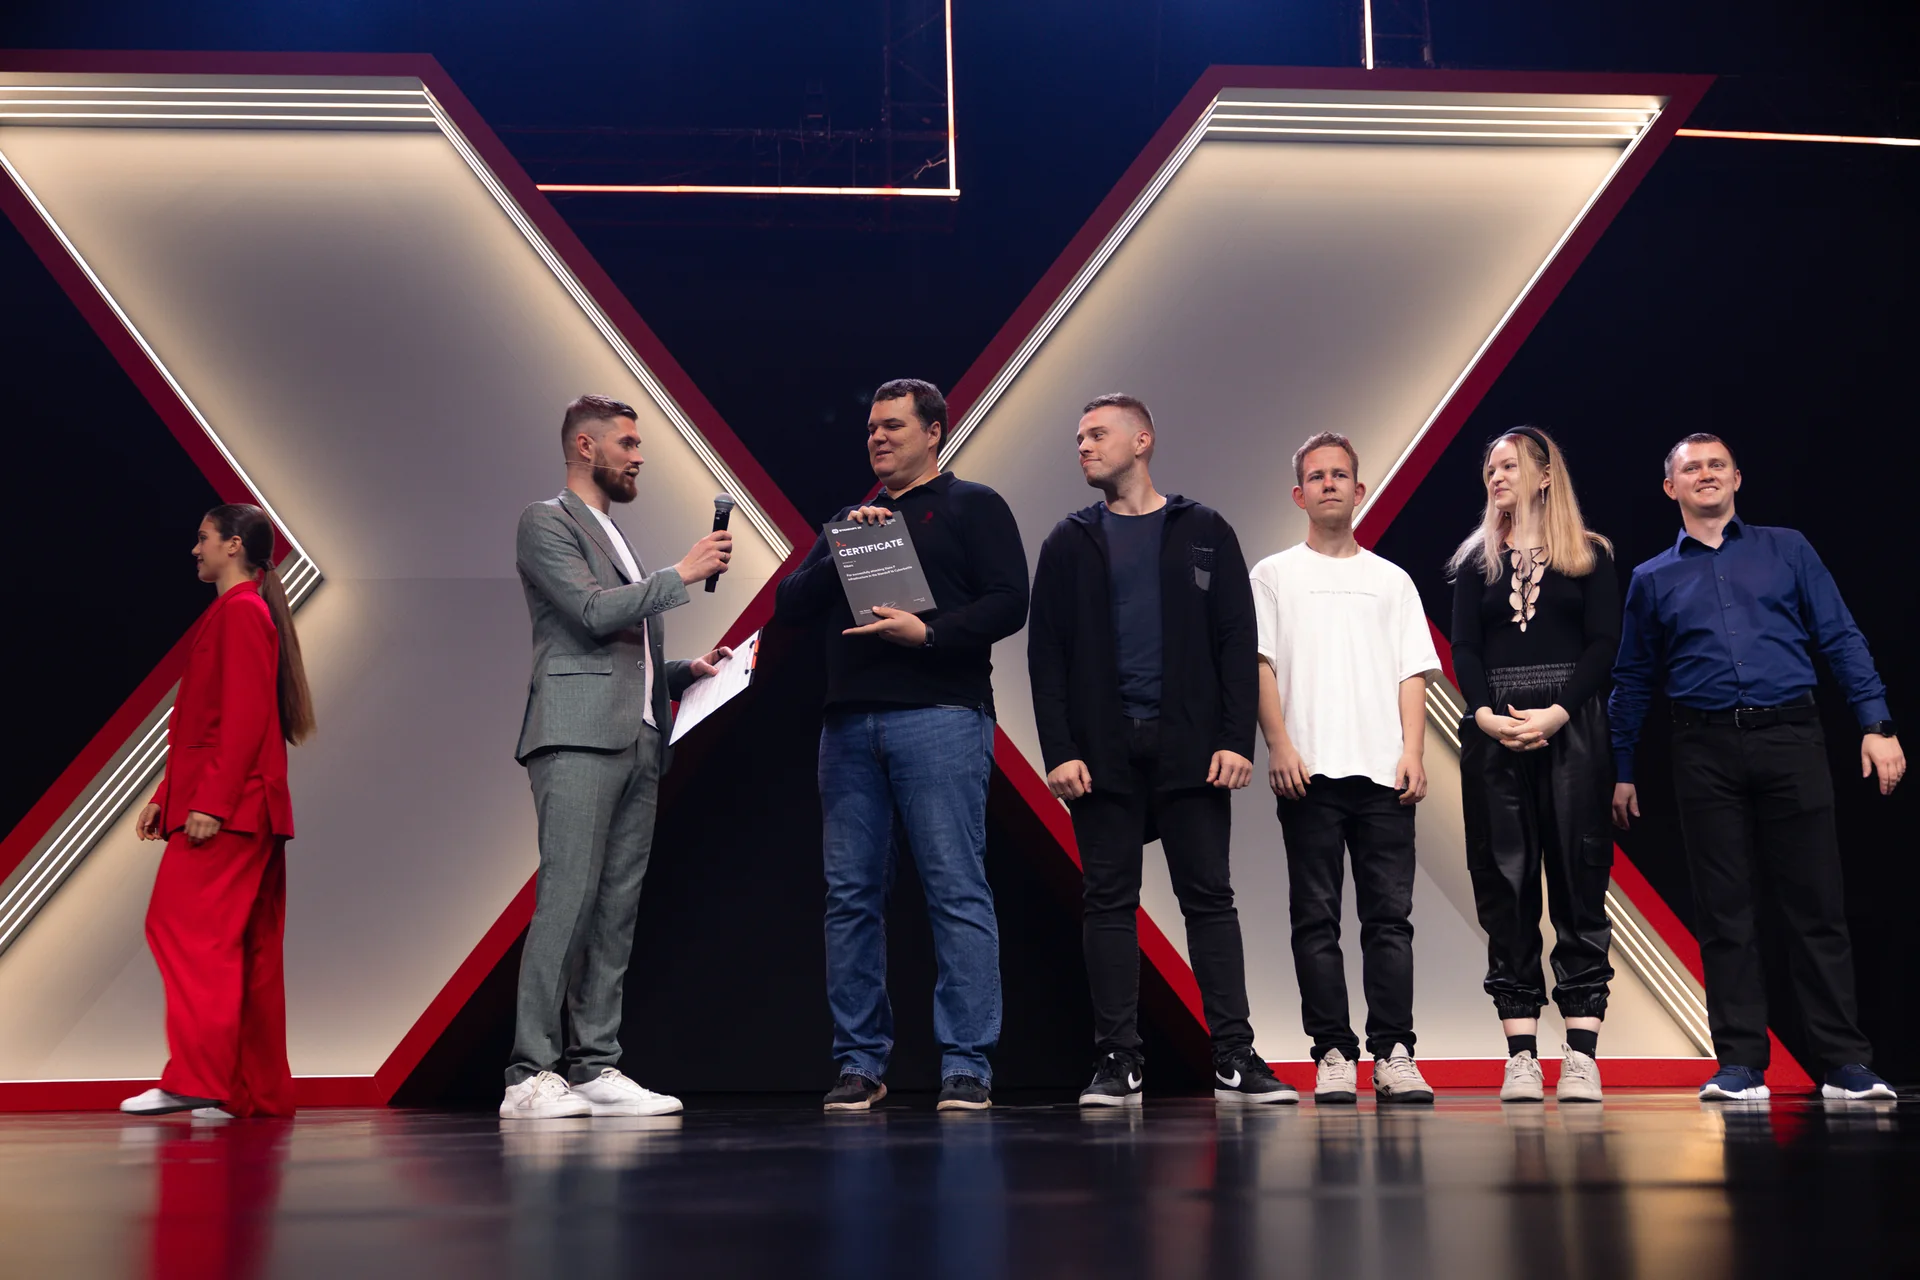
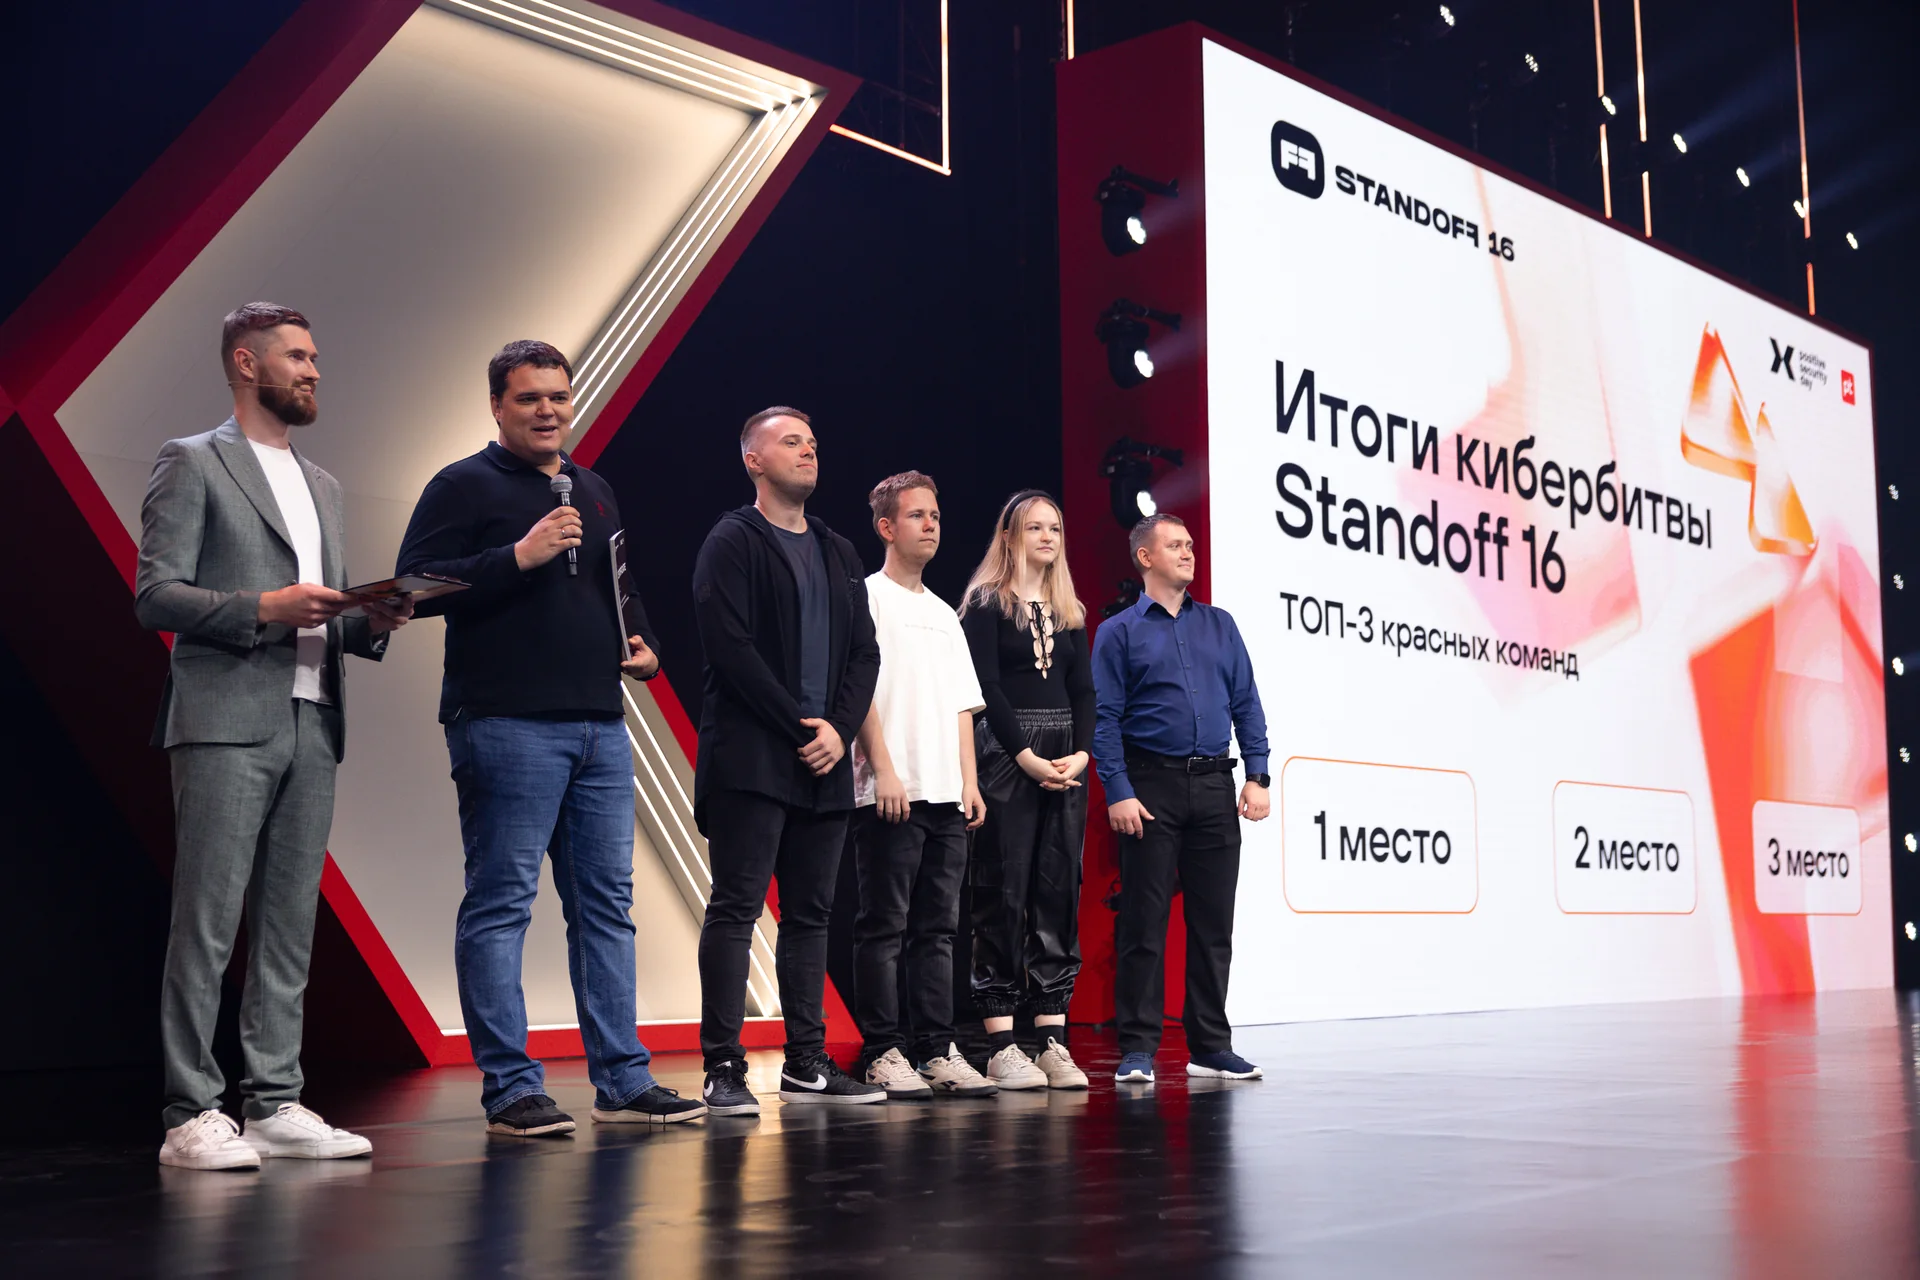
Scenes from events and day-to-day work.
For enquiries, please contact us by email.
Email — for enquiries and proposals.
Telegram — for team news and activities.
Click the email address to copy it. Shift+click opens your email client.